Showing posts with label maxmind. Show all posts

Tuesday, August 13, 2013

ZeroAccess network traffic analysis Reloaded

It's been 6 months since the last time I really sat down and looked into the network mysteries of ZeroAccess, described in my post ZeroAccess analysis part I - Network traffic.

I have seen several reports of changes to the binaries. Like this one from @MalwareMustDie and @hFireFOX
and also a couple of reports regarding the initial connect IP addresses (Commented on my blog and also by @unixfreaxjp

In the mean time the now infamous ZeroaAccess botnet have got lots of press coverage, especially for its bitcoin mining functionality, and seem to be as big if not bigger than ever. Reports vary in number, as always, but a fair guess is probably close to 10 million bots these days. The ZA botnet comes in two variants. One for bitcoin mining and one for click fraud.
So lets see if the betwork traffic from these bots have changed much or not:

1. The bot wants to know where in the world it's installed

This is done by a geoIP lookup towards the maxmind geoIP database. DNS lookup and HTTP query for lookup expected.


 Thats excactly the first thing that happens.  The geoIP lookup contains country code, city, metro code and so on, but I guess that only country code is used.

2. Install and report

The bot is then expected to install itself and report back. Last time it reported back to 194.165.17.3 this time it has switched to 194.165.17.4.


The udp payload is port 53, but not DNS. Lets have a closer look: 

080e745d8e9c9e9853765c3529717a624e1d7ced

Looks like ZA have done little to further obfuscate the install traffic, but lets xor it it with the key, which is "LONG" and bit rotate for every iteration:

4f403b110L0000004e4f610413030000aL938f98
Byte 0-3: should be bot id
Byte 8-9: country code - in this case NO 
Byte 10: 61 OS version

The early conclusion was correct. Still reporting the same info at install time using the same XOR key and scheme.

3. Flashplayer install

For some reason the bot goes on to update the flashplayer


This is where the update ends on my virtual system. Not perfect...


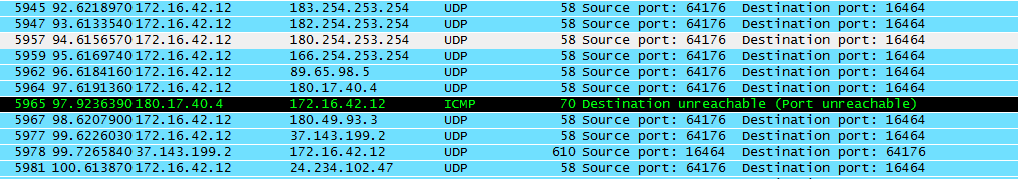
4. Start to find alive supernodes

The bot want to get fully operational and starts looking for live Supernodes. The initial IP's are probably hardcoded. Some of them are actually the same as six mionths earlier. UDP to port 16464 is still the method used by the bot. The first hit on a supernode on udp port 16464 automatically shifts the communication to TCP on the same port. 

This should be requests to get P2P lists. Lets look inside:

UDP payload: 463fdb8b28948dabc9c0d199f08c0f06

We recognize this from earlier analysis as byte 4-7  (28948dab) wil be Lteg when XORed with the correct key(ftp2) and bitwise rotated left. No change here either.
The TCP traffic is the same as well. Update plugins:

cb:00:00:80:09:b5:28:3f:00:5c:00:00 -> get file 800000cb
01:00:00:00:3b:cd:03:3f:90:03:00:00 -> get file 00000001
00:00:00:80:9e:e2:0c:3f:00:2e:00:00 -> get file 80000000

The requests have not changed at all!

The answer is encrypted plugins.

5. Continue the search for P2P lists

The getL command should be answered with a retL command:

Payload:
ef81564b28948dbec9c0d1998381a333d9fcb8984c068eceb7ece3623319383a3fed8f8bcc64e0e850443f2e339381a3a2a0fcb8ce4c068e581cf3e33a3319382f0acd8fe8cc64e0bbdb363fa33393810525d9fc8ece4c0641bd66f3383a3319288998cde0e8cc649925673681a3339370b699d9068ece4c50f9636619383a3365af8a9964e0e8ccbc192f669381a333250347674d068ecea2c11fa2a31a383ad2861bf1a448b786028d5cb7d3d927365ae701cb7bed89249525050bc3fd1b8f248f0027ce034fc52381ad7840104cf42092c55eacf96752315437cab6bd3b71838f90170723f159ef3ca6540f96849f739d96aadf1832520574c434353c774c6ad7aac9d00443a0707b0480d3e80352030a1411e5122714ba999cd21f67cc00663270f45286ecd799e7c0d1fb231230a899f2d9a79dc04eeaa1f950a16cd023501d6fd2c79b80ace52ad4eacc427379f0b75340880d43f5baf61497927c7dacc8e5165b191021be60b0da569954efa64bda7be8b83f46804c281ac0dcea96111509315824a92e84effb50a25237b06637ebd273771c9a15c3278a2cd36b819d3e754bd50692608dffd5c7bef89381236e932b78ce10068e23a764a17c91aef689cbae1e3a80e27d7b1b116ea51703388ddeb8703d1ce920b860102e7423f1f5f8a3b1e3b553d50f39ea11b9890d1172898056fc5683c02f7c5919e6da431d6be66dafc61ddae2f85f73562f7d011aeee098bf4bffce520a86204cf7fa7e381fb4911b139c269b8cec57e659d95870bb9ed74977a33623bb

Decrypted payload:
ddf1222dc445726000000010000000fffffff0000000e02feff000000009f5fdff00000009dcf8ff000000056cf8ff000000055cf8ff00000000bc5f6ff0000000a26f4ff0000000224f4ff00000000d05f2ff000000008d5efff00000000945efff0000000317efff00000000c55eeff000000007f5edff0000000597edff00000000030000001000000bd33cf09003000044bbb568c672e5b49c4690ae645ad132cc051bfaa808bc09179ef2c7050e932576f2bc5228f418633ef25d67f5e35d22372b54d92ec6a8e870868f3fbf625e7cb3d3dfd2fed3e5873cb0a71dcfd996fc1e98096d52c044d7f875eafd44bbeca9bb5b9d4069a0612509537694a91aa35209f82c7ef43a0000000e29cef00e0020080c3b39ffc1bef9166d0c7738f54c9b5fc91b4b2d725f7245ce433dba1f16078eb7d07543630fc306bad6b8a6ae454b891706998fdfae01a36f4871cf5d8d4c9e1e1b8bc80447398c5d2ac222779453e094648c6b213b8c1b6135511e89514ba341b1ab5621902e977b875b413a6c0f586c671f0b0c000009b5283f0c00500eeb83d66247aebfdad9c6e2cd64d8a2a88ed6400299cab99e73b3d2a526a4fd8922c9421cc8787d1d55bb196b9bf83088e02a12a781ca3500d0e6305744f8c37b27584ddb10d9a7a3406397b68e0e98dbc69bf82c38bcc4dfc102a5c9670025d2a36b67025b4475e76982abe1c8ff9f14a30da65752

As before:

0e 02 fe ff -> 14.2.254.255 and so on...

No changes to the P2P communication either.

6. Final callback to tell the world it's alive

To register it self and letting the bot herder know the bor is ready it fakes ntp traffic


7. Conclusion

Even if the ZA binary and the obfuscation/camuflague of the malware binary and downloads do keep on changing it seems like the communication and the botnet main features stay the same.
No changes has really occured in the past 6 months. This is good for us, the good guys, trying to protect networks and clients as it is an easy task to detect ZA activity on a network. The installation, P2P traffic and call home traffic are all covered in my previous posts on ZA. 


This means we can move on to new analysis again and just relax and know that we do catch ZA on our networks.

Thanks to @MalwareMustDie for providing the sample for research.

Happy relaxing :)

Post publish refernces:
Symantect  - ZeroAccess Modifies Peer-to-Peer Protocol for Resiliency

Sunday, February 17, 2013

Zeroaccess analysis part I - Network traffic


I have seen quite a lot zeroaccess lately. I got curious and had too look more into what this piece of malware was up to. This first part will cover network traffic stuff mainly. I will post details on other stuff later...


Updated analysis 2013-08-13(even though not much have changed)

So what will happen, on the network, after a typical Zeroaccess infection:

1. During install the bot want to lookup what country it is located in. This is done with geoip lookup @ maxmind. 


So the first thing needed is to lookup j.maxmind.com. Here is the dns q:


And then the geo ip lookup


2. The bot will then continue installing and report back to a C&C server the install status:


This is done over UDP port 53 to, what seem to be a hardcoded addresses:

194.165.17.3 -> amazingly not blacklisted -> http://bgp.he.net/ip/194.165.17.3#_rbl
66.85.130.234 -> not blacklisted either -> http://bgp.he.net/ip/66.85.130.234#_rbl

This is not DNS traffic as indicated by wireshark but XOR encrypted traffic from the bot on UDP port 53.

The UDP payload:

first packet to 194.165.17.3:
e2:91:81:fb:8e:9c:9e:98:53:76:5c:37:f9:70:7a:62:cf:70:2e:0a
first packet to 66.85.130.234:
e2:91:81:fb:8e:9c:9e:98:53:76:5c:37:f9:70:7a:62:cf:70:2e:0a

This is XORed with the key intial key "LONG" and bitwise ROL for each 4 byte:
decrypted:  a5dfceb7000000004e4f6106c3020000bb94dace

Second packet UDP payload:
encrypted:  e2:91:81:fb:f7:9c:9e:98:53:76:5c:37:f9:70:7a:62:08:cd:33:08
decrypted:  a5dfceb7790000004e4f6106c30200007c29c7cc

Third packet UDP payload:
encrypted:  e2:91:81:fb:0c:9c:9e:98:53:76:5c:37:f9:70:7a:62:58:b8:73:d1
decrypted: a5dfceb7820000004e4f6106c30200002c5c8715

Some parts of the payload seem to be static:
Byte 0-3 : a5:df:ce:b7 - Probably botid
Byte 8-9: 4e:4f - Country Code
Byte 10: 61 - OS version
Byte 11-13: 06:c3:02 -

When the inital install is done:

3. The bot will start to contact supernodes on UDP 16464:


These addresses are hardcoded in the bot at install time.
The payload in the UDP 16464 packets is a requst for updatet P2P ip address lists. See below for further analyzis.

4. The first hit on UDP will kick in TCP and in this case the bot starts talking to: 50.137.49.12 on port 16464


50.137.49.12 -> blacklisted by spamhaus -> http://bgp.he.net/ip/50.137.49.12#_rbl

So what is happening here?

Three TCP sessions are established towards 50.137.49.12 all on destination port 16464.
Seem to be download of plugins/dlls to enhance functionality

src port 49988 - first session:

Only two packets with payload; one request and one response packet:


First data packet over TCP from the bot to 50.137.49.12: payload length 12
01:00:00:00:71:5b:2a:3e:a0:03:00:00
Which means:
requsting file 00000001
timestamp: 3a2a5b71
length: 000003a0

First data packet from server(50.137.49.12) to bot:payload length 928
encrypted:
6d:91:19:d2:60:1a:49:f8:e7:5a:c2:d6:46:55:b0:59:28:8a:f3:72:9f:3a:e5:62:29:f3:67:0e:8e:68:08:a9:1b:d2:eb:cd:55:98:2a:09:f8:93:71:6d:28:4a:71:8a:14:d0:fe:a2:95:08:f7:6c:07:e5:4f:85:08:39:fe:87:dc:26:b1:bd:17:15:5e:76:9b:ea:2f:42:ab:0c:45:e3:c0:35:10:f0:26:e2:65:ea:9a:d8:74:5b:04:92:88:c0:04:08:d8:2a:ce:94:71:ab:48:38:ca:76:a8:ec:a7:05:e8:e0:4c:17:3d:6a:3b:82:11:b6:99:c8:82:c5:99:d2:7f:69:0f:86:a5:7a:8a:86:9c:4b:56:df:30:1e:e4:66:1e:8c:51:98:73:39:55:38:8b:dd:8e:95:bc:ae:5b:66:68:09:e2:b7:b8:3e:75:5b:1b:26:b6:3d:4b:b5:59:14:b8:6d:05:36:e1:4d:97:8b:15:c7:79:98:ff:69:c9:1d:27:ae:f1:6c:94:41:d8:f2:c4:d9:0c:0e:9c:f5:23:9f:99:41:64:a4:d1:33:9b:12:ae:90:04:8d:88:92:29:fe:66:63:f7:e5:4e:fa:b0:f6:04:51:c0:41:42:73:f9:6f:b3:54:da:79:32:47:3f:76:ca:ec:3b:40:21:31:ae:1b:b0:8f:5c:e5:64:6d:b9:27:6c:47:7f:de:b8:d2:27:6c:56:6e:e9:aa:5e:a1:17:bd:9f:77:51:ef:72:17:78:73:c9:cd:95:1a:58:d3:c2:6c:72:71:28:78:eb:be:e4:81:33:3f:10:62:7e:33:7e:1c:0e:15:6a:23:08:75:75:e9:7d:02:33:00:77:a4:1b:60:dd:bc:a2:59:f2:73:81:01:33:b1:d7:9a:84:53:da:e0:b6:69:fd:dd:f0:7d:6d:6b:8f:10:79:ee:94:6e:00:6e:1e:1f:32:a2:20:cd:7a:56:c6:3b:c8:0d:d5:6b:38:72:b2:b5:a6:c3:c1:66:dc:3f:68:58:57:67:16:39:70:7b:ea:0a:59:8c:ff:45:2e:56:1b:a6:5e:4e:85:d4:ac:b1:05:03:ba:8d:31:15:f1:19:e0:40:1b:03:ff:20:45:d3:59:66:0e:f6:ba:48:bd:55:55:86:82:8b:7e:16:e3:a2:6f:37:52:74:81:a6:bb:ca:6b:1c:3c:3a:30:75:57:95:81:d1:e1:22:04:7e:6b:d0:b5:38:6e:ec:1f:2f:8f:cb:bb:d3:d4:a2:54:f1:5b:9c:e7:55:d2:98:04:98:b6:d1:df:75:30:a9:c4:ea:dc:97:14:46:43:de:2d:25:bf:c0:6c:0d:f6:f1:1e:03:68:45:b7:a3:41:ef:53:98:22:16:ad:7d:28:d4:8e:5b:69:83:aa:b1:ef:3d:7d:ae:e9:fb:a1:0d:db:ee:ea:e7:d6:b2:ab:e6:ca:a9:68:16:81:33:22:8c:af:a8:b0:42:76:ed:cf:4d:5a:f5:ef:01:73:49:b7:15:67:4a:ce:da:c0:85:6a:6d:12:c1:f4:d0:5a:6c:34:92:ad:15:fb:91:6d:5f:ea:4b:ab:59:dd:43:22:87:45:d1:70:0e:30:54:c8:73:3b:0f:f3:e9:86:fc:5f:b7:ce:01:97:1c:91:f9:70:03:b2:f1:79:59:5e:08:c6:0b:6f:3c:94:23:8c:65:a5:de:db:82:8d:bc:14:2e:95:44:75:4b:c7:40:87:90:5a:45:56:06:d7:1c:83:e6:fe:7e:33:ac:5d:cd:00:24:a1:16:a7:7f:da:b0:74:af:4c:4a:1e:02:d3:6b:c7:4c:1a:21:b5:1f:92:fc:57:b6:6d:0f:0c:b0:b3:50:dd:4b:9b:50:e5:7f:31:d8:20:15:7c:b9:51:a8:28:5d:e9:1e:0c:db:2c:5e:84:43:4e:ca:fa:ec:9c:ff:97:7f:b4:b5:34:a4:c3:70:bb:74:d1:f9:15:2a:cd:55:15:7e:c9:aa:ed:63:a7:a7:9f:4f:3f:a5:33:9f:20:72:07:cb:21:69:72:8e:24:bd:2e:2c:12:5e:ac:6f:19:b0:5e:c2:bf:53:da:7b:87:ba:14:e2:69:60:50:57:96:3f:27:46:21:1c:e7:ed:8c:45:2b:44:2f:dc:b2:9a:2f:a6:6a:f9:05:4e:07:d9:52:df:8c:98:8c:c3:37:75:6b:b7:c9:54:d1:fd:14:e2:83:2e:99:16:a1:b9:17:fd:f8:01:39:c7:38:8f:41:92:d5:94:f5:de:0c:17:ea:29:e1:f0:6e:2e:84:90:71:97:ed:14:b7:d8:b4:4d:92:90:43:cf:5f:64:4e:c0:45:03:47:95:8a:a3:0b:18:eb:e8:4f:0f:de:58:88:d9:a7:30:68:51:f3:b0:05:d9:1c:44:ab:3d:af:4a:80:1e:cc:b6:49:2c:5f:c1:90:7b:8c:20:2b:90:98:d4:d3:c3:0a:5b

RC4 encrypted dll.

src port 49989 - second session:


Second data packet source port 49989: payload length 12
encrypted: cb:00:00:80:8f:17:90:3d:00:54:00:00
filename: 800000cb
Timestamp:
size: 00005400

Reply data packets from server(50.137.49.12) to bot: 
Click fraud plugin/dll. RC4 encrypted


src port 49990 - third session:


Third packet:
encrypted: 00:00:00:80:ad:03:be:3d:00:2e:00:00

Get the file : 80000000
timestamp:3db303ad
filesize: 00002e00


Reply data packets from server(50.137.49.12) to bot: 
Phone home plugin/dll

5. Next step then is C&C callback to tell the botmasters I'm alive:


UDP 123 traffic towards 194.165.17.3(again) and 91.242.217.247
Both packets have the same payload:
encrypted: 47:4e:01:03:8e:9c:ad:f9:de:3b:3d:31:9f:ad:b4:d5:20:ab:e2:be

Which once again is XORED with the key "LONG" and again ROL
decrypted: 00004e4f00003361c3020000a5dfceb7544f167a
decr ascii: ??NO??3aÃ???¥ßηTO?z

Byte 0-1: 0000
Byte 2-3: Country Code
Byte 7: OS version
Byte 12-15: bot ID

6. Now lets keep our P2P address lists up to date:


The "fingerprint" of Zeroaccess. calling supernodes on UDP port 16464 once every second.
The bot here requests updated IP lists from it's peers. XORED 4 Bytes at a time with the iniyial key "ftp2" and then bitwise ROL for each XOR operation.
payload of the request packet:
encrypted: b8:14:35:fe:28:94:8d:ab:c9:c0:d1:99:85:95:6f:3f
Decrypted: 8a6441984c746567000000001614cc0c
decr ascii: ŠdA˜Lteg??????Ì?

Byte 4-7: command -> getL for get updated List

The supenode will then answer(with an XORED payload like the request):
encrypted:
3b:bb:d0:88:28:94:8d:be:c9:c0:d1:99:83:81:a3:33:f8:fd:ba:99:4c:06:8e:ce:57:f2:e1:63:33:19:38:3a:d8:cc:8d:8a:cc:64:e0:e8:2f:37:3d:2f:33:93:81:a3:d3:d8:fe:b9:ce:4c:06:8e:3b:67:f1:e2:3a:33:19:38:f3:98:cf:8e:e8:cc:64:e0:9c:77:12:9d:a3:33:93:81:03:84:c6:67:8e:ce:4c:06:68:56:49:49:38:3a:33:19:11:1c:6d:bb:e0:e8:cc:64:ad:b1:b8:47:81:a3:33:93:26:4e:b3:a8:06:8e:ce:4c:c6:5b:18:b3:19:38:3a:33:42:18:b9:fd:64:e0:e8:cc:11:3c:e2:b1:93:81:a3:33:25:03:47:67:4d:06:8e:ce:e8:57:36:a3:93:1a:38:3a:c8:97:49:05:05:cc:ea:c7:7d:c1:2c:89:7b:22:2f:1c:5d:67:9b:3b:33:b9:66:cf:ab:8b:ff:ff:24:fd:6d:15:59:be:19:2d:0a:4b:cf:c8:5a:5d:e4:4d:a9:0d:06:20:38:a7:de:ec:25:21:d4:14:ca:51:05:3d:c6:33:15:70:6b:07:71:e1:2d:59:31:5f:80:a2:5e:55:18:6c:70:e4:8b:3a:e2:50:7e:6a:26:20:c2:6f:66:f1:3d:a9:06:25:74:e3:7b:73:0e:1f:25:2e:96:81:a9:48:9b:0b:27:70:70:33:9c:ff:d4:c5:8f:c6:8b:1c:66:1b:d2:6c:fd:9e:66:32:70:f4:61:67:5e:d5:99:e7:c0:d1:dc:7c:59:96:17:d0:0a:1f:7b:bd:9d:a1:af:6b:20:63:c2:26:e0:19:3f:3c:19:9d:ee:38:d7:60:73:4c:3c:21:6a:6d:d8:01:cd:50:55:2a:59:43:8b:49:80:0c:18:24:ad:d6:dd:92:54:02:f9:85:db:21:a7:91:9f:72:ea:29:97:7e:b1:c0:b0:54:83:33:06:8b:e1:8b:1c:cd:21:d9:13:1f:49:95:9e:5a:44:d7:21:25:49:ba:ff:c5:3f:ab:3c:e3:d8:3f:50:1a:db:0e:bf:d9:6c:c0:fc:1f:5d:62:67:c3:c2:a1:fe:1f:1f:83:48:14:d1:50:24:d5:d0:b4:f8:93:81:23:e8:31:93:7a:ce:18:06:8e:ff:a2:32:5f:08:52:77:7b:15:6f:da:dc:9c:53:55:27:cb:2c:91:f7:32:ff:97:aa:ee:d0:82:9c:6a:b0:19:24:b1:96:17:f6:a3:34:48:f8:a4:ba:bb:71:a3:77:cf:1c:fc:76:f0:d9:60:d1:0d:26:c0:65:6f:11:1e:de:31:b1:6b:12:11:d3:dc:e5:cf:be:fa:27:24:86:86:c4:40:ae:33:18:22:8c:ff:d3:3a:4a:ea:ef:20:80:9a:af:82:14:31:b1:36:ff:ac:90:e8:e2:9a:80:1f:86:9e:8f:ae:93:af:29:dc:4c:73:34:c8:48:67:1b:9e:d0:d7:8a:be:ee
decrypted:
09cba4ee4c7465720000000010000000defefdfe00000000cefefdfe00000000befefdfe00000000b6fefdfe00000000b4fefdfe00000000a6fefdfe0000000087fefdfe000000004deedb5d0000000044e3e0640000000074cbd0450000000061680b89000000006d60218e000000002509d48e00000000ca47852a000000007068cd9b00000000d8fc3328000000000300000001000000715b2a3ea0030000aea53971c9a80a2fe408ec5848b1aebf3a41987cfdf560413612f3e31ece742d2dd82b5de287ab288bc42d8d0a3e95a17fc0f8efabef9812d6cc9c31fe0926691b7317d3cdb1fd3b4073c79c99cf4377887d857678e4e86cce73fb6824913c1646930f156affcde25f4178d1088a84435630db9898c3010812107a86e175c5a400000080ad03be3d002e0000efefd83570f60958b5f19b2f32f22c7ff815f9214b5a2bed06f4b380a2d5f5e1c95e4b808a377329d78dc74f9c91812895ecee8b24769fb73bc96bf55fa373e016dd8253b313e41500052fc710d1bc400a2773a6ac2a30b145c5a1763605ee32af627b0c76199c69f3dfe20e651341ff54dafa9b982d6ff7847031b8bd1c1065cb0000808f17903d00540000623b3e4332616e436109e8ac749f31c71ab5583791cc042ba9b7a49fe47e5522ad0b8efa9b0e7be1d4cedd43439f03783ca76910e1723eb5c32208371850fffd670e8c4ac5ddf58dc85750e0e224a862fad8f3156c529979ccec67e7d6a90cdaa8bd2a629f89d0d8fcb26ff252eb4e7b36e01c9d40a749eb003d9d9719c6b860

Explanation:
Byte 4-7: Lter -> retL - returning list of peer IP addresses
Byte 16 and onward: IP address of  peer supernode and timestamp since last update. Timestamp is in seconds. Here all are updated within the last second.
defefdfe00000000 -> 222.254.253.254
cefefdfe00000000 -> 206.254.253.254
befefdfe00000000 -> 190.254.253.254
b6fefdfe00000000 -> 182.254.253.254
b4fefdfe00000000 -> 180.254.253.254
a6fefdfe00000000 -> 166.254.253.254
87fefdfe00000000 -> 135.254.253.254
4deedb5d00000000 -> 77.238.219.93
44e3e06400000000 -> 68.227.224.100
74cbd04500000000 -> 116.203.208.69
61680b8900000000 -> 97.104.11.137
6d60218e00000000 -> 109.96.33.142
2509d48e00000000 -> 37.9.212.142
ca47852a00000000 -> 202.71.133.42
7068cd9b00000000 -> 112.104.205.155
d8fc3328000000000 -> 216.252.51.40

7. With this information we are able to map this botnet issuing commands to the supernodes to give us the IP lists they have :)

Look at my post "Zeroaccess supernodes mapped - part I" for IP's of Supernodes

Check out this post to check a remote host for ZeroAccess infection.

8. There also is a newL command to insert new nodes into the botnet.


Sophos have analyzed this well back in Sept 2012 - Link